Glossary
WAF
Web Application Firewall — A security control that filters, monitors, and blocks HTTP traffic to and from a web application, defending against common attacks like SQL injection and cross-site scripting at the application layer. Unlike a traditional network firewall, a WAF inspects the content of web requests rather than just ports and protocols.
Recent coverage mentioning WAF
WordPress RCE Exploited via CVE-2026-14894 & CVE-2026-32475
Attackers exploit critical RCE flaws in WordPress Super Forms (CVE-2026-14894) and Elementor Pro (CVE-2026-32475) to deploy web shells and seize sites.
Cloudflare Enhances Vulnerability Management with AI & Context
Cloudflare introduces a new service leveraging AI and real-world operational context to prioritize and remediate vulnerabilities in customer codebases.
CVE-2026-72529: Critical RCE in TrueConf Server via Missing Auth
CISA warns of active exploitation of CVE-2026-72529 in TrueConf Server, allowing remote attackers to execute arbitrary scripts via port 4307/TCP.
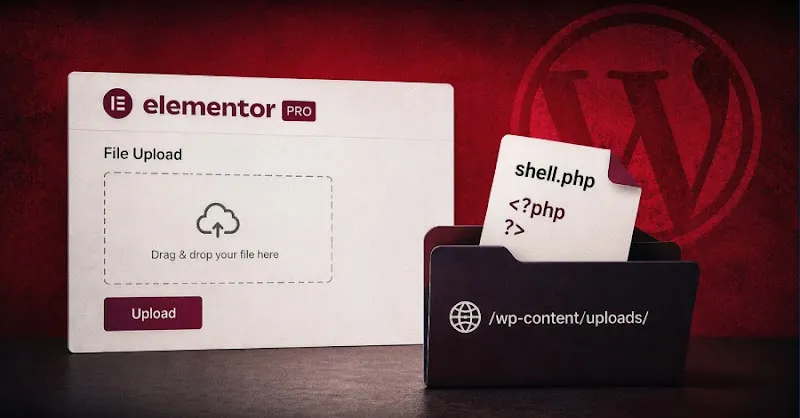
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.
BdThemes WordPress Plugin Supply Chain Attack Creates Rogue Admins
A supply chain attack on BdThemes WordPress plugins exploited an XSS vulnerability, creating stealthy rogue admin accounts and webshells.
CVE-2026-60137: WordPress Core SQL Injection to RCE — Patch Now
CISA warns of active exploitation for CVE-2026-60137, a WordPress Core SQL Injection vulnerability chaining to RCE for unauthenticated attackers.
Advertisement