Advertisement
Android Nov 2026 Updates Patch Critical RCE CVE-2026-58868
Google's November 2026 Android security updates address over 200 vulnerabilities, including a critical RCE in Framework (CVE-2026-58868) requiring immediate patching.
XCPE Botnet Takedown: 1.3M Android TV Boxes Hijacked for Proxies
Google and partners dismantled the XCPE botnet, which compromised 1.3M+ Android TV boxes and IoT devices, turning them into residential proxies for criminal use.
XCPE Botnet Dismantled: Android OEM Videostrong Implicated
Google and partners dismantled the XCPE botnet, tied to Android OEM Videostrong, which infected 1.3M set-top boxes for ad-fraud and proxy networks.
x.cpe Backdoor in Videostrong Android TV Boxes: Google Takedown
Google disrupted a 1.3 million-device Android botnet, attributing its origin to a pre-installed backdoor, 'x.cpe', in Videostrong TV boxes.
Ephemeral Tampering: UNC7017 Exploits AOMEI Update Systems
Google and Mandiant detail UNC7017's short-burst supply chain attacks on AOMEI update infrastructure, deploying CROSSROAD and SHINYROAD malware.
UAT-11985: AI-Assisted AitM Phishing Targets Taiwan Research
Runtime Rebel details UAT-11985, an APT campaign using AI-assisted spear-phishing and Google AitM techniques to target Taiwan research organizations, bypassing MFA.
Hackers Hijack Google & Others' Domains via ccTLD Registry Breach
Hackers compromised ccTLD registries, enabling DNS hijacking of Google and other brands' domains and unauthorized HTTPS certificate issuance.
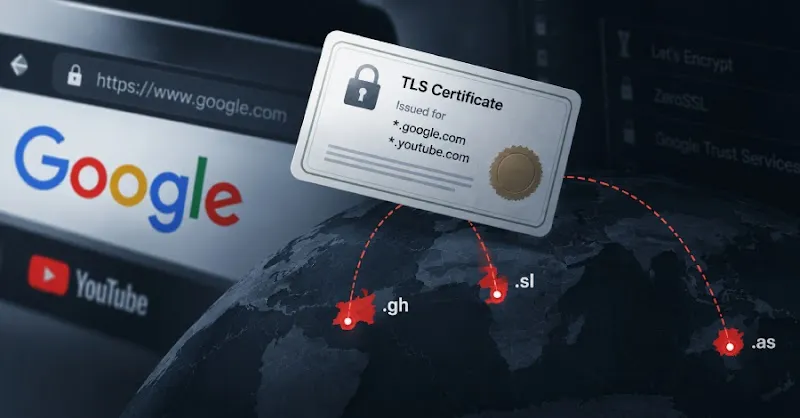
ccTLD Hijacks Force Unauthorized Google HTTPS Certificates
Attackers hijacked .gh, .sl, and .as registries to obtain unauthorized HTTPS certificates for Google domains via DNS manipulation.
Google PageBreak AI Agent Uncovers 500 Web App Flaws
Google's PageBreak AI agent identified over 500 flaws in its own web applications, showcasing the growing trend of AI-driven vulnerability discovery.
Google Pauses OSS Bug Bounty Due to Automated Invalid Reports
Google temporarily paused its Open Source Software Vulnerability Reward Program for product vulnerabilities, citing a surge in automated, invalid submissions.
Critical Citrix NetScaler Zero-Days: CVE-2026-88772 & CVE-2026-88771
Mandiant and Google identified active zero-day exploitation (CVE-2026-88772, CVE-2026-88771) in Citrix NetScaler ADC and Gateway, leading to root access.
AI's Impact on Vulnerability Discovery & Exploitation Trends
Google Threat Intelligence reports AI is doubling vulnerability disclosures and exploitation, shifting focus to more consequential flaws including RCEs.
Malicious Custom GPTs Used for RAT Delivery via ChatGPT Lures
Threat actors are leveraging malicious custom GPTs on ChatGPT and Google domains as lures to deliver Remote Access Trojans (RATs) in ClickFix-style campaigns.
ClickFix Variant Leverages Google API for Crypto Theft
A ClickFix social engineering variant abuses Google Visualization API and Google Sheets for C2, injecting web skimmers into browsers for cryptocurrency theft.
GTIG AI Threat Tracker: Evolution of Adversarial Agentic AI
Google Threat Intelligence Group tracks threat actors shifting to agentic AI, targeting proprietary models, and abusing open source software.
Chrome Zero-Day CVE-2026-85046 Actively Exploited: Patch Now
Google released an urgent update for a critical Chrome zero-day, CVE-2026-85046, actively exploited in V8 engine type confusion attacks.
Google, Anthropic, and OpenAI Launch Cyber AI Models and Safeguards
Google, Anthropic, and OpenAI unveil advanced cybersecurity AI models like Gemini 3.8 Flash Cyber, focusing on defense and strict access controls.
Microsoft Defender Blocks Legitimate Google Search Links
Microsoft Defender for Office 365's Safe Links feature is incorrectly flagging legitimate Google search results as malicious, blocking user access and generating alerts.
ToxicPanda 2.0 Android Malware Abuses Wireless ADB and VPN
ToxicPanda 2.0 Android malware uses VPN permissions to block Google Play and abuses Wireless ADB to gain shell access and deploy overlays.
Russian Threat Clusters Abuse OAuth and WhatsApp for Espionage
Google Threat Intelligence reports three suspected Russian groups using OAuth phishing, Google app passwords, and WhatsApp device linking to hijack accounts.
Encrypted Prompts Bypass AI Safety Guardrails in Grok and Gemini
Researchers discover cryptographic context injection, a novel technique bypassing AI safety filters in xAI Grok and Google Gemini using encryption.
Russian Threat Clusters Target Academia and Government via Auth Abuse
Google Threat Intelligence Group tracks three Russian cyber espionage clusters abusing legitimate authentication flows and app passwords.
Chrome, Firefox, Thunderbird Updates Patch Dozens of High-Severity Flaws
Google and Mozilla release urgent updates for Chrome 151, Firefox 154, and Thunderbird 154, addressing critical and high-severity vulnerabilities including RCE.
Agentic Source Code Review: Scaling Vulnerability Discovery with AI
Learn how Google Mandiant uses the Agentic Vulnerability Discovery Harness to accelerate secure code review and find critical flaws at scale.