Advertisement
MAccConc: Memory Access Concurrency Testing and Tracing Tool
Explore MAccConc, a new developer tool for testing and discovering Linux kernel race conditions using memory access tracing and stack delays.
North Korean Hackers Deploy New Linux Espionage Toolkit
North Korean state-sponsored hackers target automotive and media firms in South Korea using a custom Linux espionage toolkit.
CVE-2026-53362: Linux Kernel IPv6 Privilege Escalation
CISA adds CVE-2026-53362 to KEV, confirming active exploitation of a Linux Kernel privilege escalation vulnerability via IPv6. Patch now.
Linux Foundation to Govern TRACE: AI Runtime Attestation Standard
The Linux Foundation now governs TRACE, an open standard providing hardware-backed, verifiable evidence for AI agent runtime and confidential workloads.
Trojanized npm Packages Deliver AI-Powered RedC2 4.0 Linux Backdoor
Malicious npm packages deliver RedC2 4.0 Linux backdoor, featuring AI-assisted command and control for advanced post-exploitation.
UAT-10147: Agentic AI Enhances Post-Compromise Operations
Chinese-speaking adversary UAT-10147 leverages agentic AI for scaled exploitation, reconnaissance, and persistence on Windows and Linux web servers.
SPECTRE Malware: UAT-10147 Targets IIS, Linux Servers with Rootkits
Chinese-speaking actor UAT-10147 deploys SPECTRE, a cross-platform implant featuring Linux rootkit and BYOVD EDR bypass capabilities.
Evooo1Bot Linux Botnet: Beyond DDoS with Exploits & Credential Theft
Evooo1Bot Linux botnet evolves, adding exploitation modules, credential theft, and SOCKS relays, transforming compromised devices into persistent attacker infrastructure.
Evooo1Bot Linux Botnet Turns Routers Into SOCKS5 Relays
A new Mirai-based modular Linux botnet called Evooo1Bot targets internet routers, turning them into SOCKS5 traffic relay nodes.
TONTOU CPU Attack Bypasses Spectre v2 Mitigations on Linux
New TONTOU CPU attack bypasses Spectre v2 fixes on Intel and AMD, enabling unprivileged attackers to leak Linux kernel password hashes.
NatJack Attacks: Exploiting NAT Trust in Windows, Linux, macOS
Synack's research reveals NatJack attacks, a new class of NAT exploitation affecting Windows, Linux, and macOS, leveraging trust assumptions.
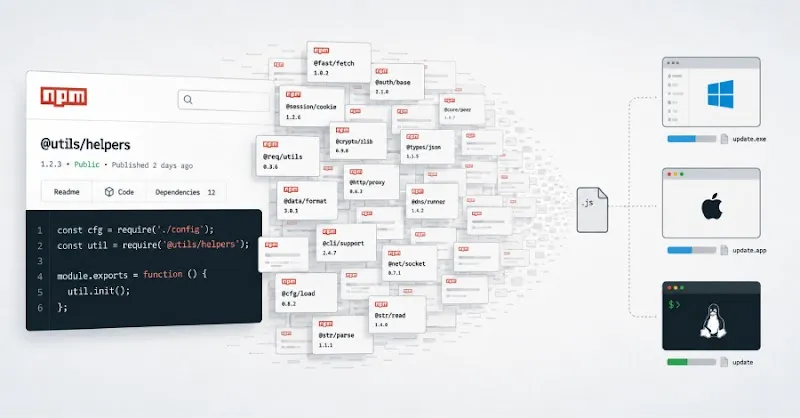
Critical npm Supply Chain Attack Delivers Cross-Platform RAT/Infostealer
Critical npm supply chain attack involving nearly 800 malicious packages delivers WEL1DROPPER RAT and infostealer to Windows, macOS, and Linux users.
Linux Shell Forensics: Investigating Atuin History in Incident Response
Forensic analysis of Linux shell history using Atuin, a tool that enhances command logging.
CVE-2026-64561: Zapscape KVM Flaw Allows Guest VM Escape
Analyze CVE-2026-64561, a KVM shadow MMU vulnerability dubbed Zapscape allowing L1 guest VM escape to Linux hosts. Learn mitigation steps.
SSH Botnet Reconnaissance Before Linux Cryptominer Deployment
An SSH botnet performs extensive hardware and system reconnaissance on Linux targets before deploying an optimized cryptocurrency miner. Weak credentials exploited.
Microsoft Secure Boot Bypass via Vulnerable Shims — Remediation Guide
An analysis of a decade-long vulnerability in Microsoft Secure Boot. Learn how vulnerable Linux shims allow attackers to bypass UEFI firmware protections.

Tengu Botnet Exploits Linux Watchdog for Reboot-Based Persistence
The Mirai-derived Tengu botnet utilizes hardware watchdog timers to trigger reboots when its process is terminated, ensuring persistence on Linux devices.

CVE-2026-53264: Linux Traffic-Control Bug Escalates to Root Access
A use-after-free race condition in the Linux kernel traffic-control subsystem, CVE-2026-53264, allows local privilege escalation to root on CentOS Stream 9.
Multi-Threat Brief: AI Malware, Zimbra Exploits, Linux Kernel Flaws
Analysis of recent threats including DolphinX AI malware, state-sponsored Zimbra exploits, Siemens industrial switch vulnerabilities, and 400 Linux kernel flaws.

Claude Cowork Sandbox Escape: VM to macOS File Access
A critical sandbox escape vulnerability in Anthropic's Claude Cowork allows AI agents to break out of their Linux VM, gaining full file access on macOS hosts, affecting…
CVE-2026-64600: Local Root via Linux XFS Race Condition — Patch Now
A nine-year-old race condition in the Linux kernel XFS filesystem, known as RefluXFS, allows local attackers to achieve root privileges via file overwrites.

CVE-2026-64600: RefluXFS Race Condition Grants Root on RHEL Systems
Technical analysis of CVE-2026-64600, a nine-year-old race condition in the Linux XFS driver allowing local privilege escalation on RHEL and Amazon Linux.
OpenMandriva Insider Sabotage: Risks of Contributor Access Misuse
OpenMandriva Linux reports an attempted internal sabotage by a disgruntled contributor, highlighting critical risks of insider threats in open-source projects.

CVE-2026-43499: GhostLock Linux Kernel Privilege Escalation Analysis
A 15-year-old Linux kernel flaw, CVE-2026-43499 (GhostLock), enables local root access and container escape across major distributions since 2011.