Advertisement

SLH Recruits Women for $1,000 IT Help Desk Vishing Attacks
Scattered LAPSUS$ Hunters (SLH) are offering financial incentives to recruit women for vishing campaigns targeting corporate IT help desks and IAM systems.
Data Poisoning Risks in Real-Time AI Search and Ingestion
A recent experiment highlights how rapid web scraping for AI models like Gemini and ChatGPT enables data poisoning attacks through unverified web content.

Quantitative Scoring for OT Incidents: The Richter Scale Model
Analysis of a new logarithmic scoring system designed to quantify the physical magnitude and technical severity of operational technology (OT) cyberattacks.
Cybersecurity M&A Trends 2025: Analysis of 426 Industry Deals
SecurityWeek reports 426 cybersecurity M&A deals in 2025, highlighting a disciplined market shift toward GRC, data protection, and identity management.
Ex-L3Harris Executive Sentenced for Selling Zero-Days to Russia
Former Trenchant CEO James Michael Robinson sentenced to 90 months for stealing zero-day exploits and selling them to a Russian state-linked broker.
US Treasury Sanctions Russian Broker for Stolen Zero-Day Exploits
The US sanctions Artem Kruglov and associated firms for brokering stolen hacking tools and zero-day exploits for Russian intelligence services.
Advertisement

L3Harris Insider Sentenced for Selling Zero-Days to Russian Broker
Former defense contractor Peter Williams sentenced to seven years for selling eight zero-day exploits to Russian broker Operation Zero for millions in profit.

National Security Risks of Manual Data Transfer Processes
Report reveals 50% of national security organizations rely on manual data transfers, creating systemic risks and critical intelligence latency.
Interpol’s Operation Red Card 2.0: 651 Arrests Targeting Cybercrime
INTERPOL and AFRIPOL's Operation Red Card 2.0 disrupts West African cybercrime syndicates, leading to 651 arrests and $4.3 million in seized funds.
Windows 11 KB5077241: Native Sysmon Integration and BitLocker Updates
Microsoft integrates native Sysmon and enhances BitLocker management in the Windows 11 KB5077241 optional update, providing advanced telemetry for defenders.
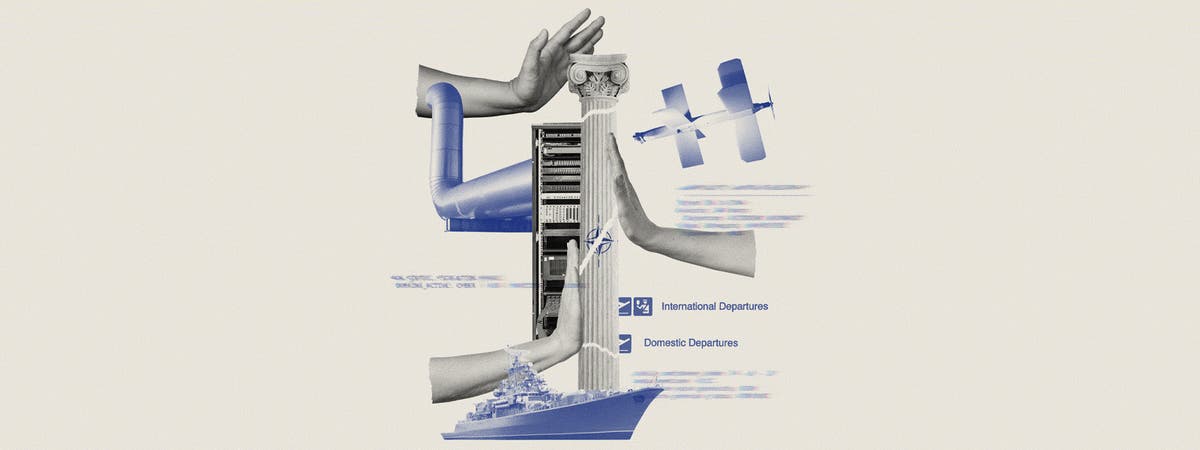
Russia's Escalating New Generation Hybrid Warfare in Europe
Analysis of Russia's coordinated New Generation Warfare against NATO, blending cyber attacks, sabotage, and influence operations. Understand the threat.
AI-Enabled Threats: Model Extraction, APT Phishing, & Malware Evolution
GTIG reports on Q4 2025 AI threats: rising model extraction, APTs using AI for reconnaissance and phishing, and new AI-integrated malware families like HONESTCUE and…
UNC6201 Exploits Dell RecoverPoint Zero-Day CVE-2026-22769
Mandiant and GTIG detail UNC6201's exploitation of CVE-2026-22769 in Dell RecoverPoint for VMs, deploying GRIMBOLT backdoor and novel VMware TTPs.
Lazarus Group Shifts to Medusa Ransomware & Multi-Tool Attacks
North Korea's Lazarus Group now employs Medusa ransomware, Comebacker backdoor, Blindingcan RAT, and Infohook info stealer in recent attacks, signaling an evolving…
Attackers Halve Breakout Time to 29 Minutes, CrowdStrike Reports
CrowdStrike research indicates attackers now achieve lateral movement in just 29 minutes, driven by credential misuse, AI, and blind spots.
Diesel Vortex Phishing Campaign Targets Logistics Sector
Financially motivated Diesel Vortex group targets US & European freight and logistics with extensive phishing campaign, using 52 domains to steal credentials.

UAC-0050 Targets European Financial Institutions with RMS Malware
Russia-aligned actor UAC-0050 expands operations beyond Ukraine, targeting European financial entities with spoofed domains and RMS malware for espionage.
AI Influence Operations and the Erosion of Democratic Feedback
Bruce Schneier analyzes how AI-generated content overwhelms democratic institutions and creates an influence arms race, threatening institutional integrity.
Spanish Authorities Dismantle Anonymous Fénix Hacktivist Node
Spain's National Police arrested four members of Anonymous Fénix, a hacktivist group targeting government infrastructure with DDoS and data exfiltration.
Lazarus Group Targets U.S. Healthcare with Medusa Ransomware
North Korean Lazarus Group is targeting U.S. healthcare providers with Medusa ransomware, utilizing Dtrack malware for initial access and persistence.

UnsolicitedBooker Targets Central Asian Telecoms via LuciDoor Backdoor
The UnsolicitedBooker threat actor has pivoted to targeting telecommunications providers in Kyrgyzstan and Tajikistan using LuciDoor and MarsSnake backdoors.

Lazarus Group Deploys Medusa Ransomware in Global Healthcare Attacks
Lazarus Group (Diamond Sleet) targets Middle Eastern entities and U.S. healthcare with Medusa ransomware, according to Symantec and Carbon Black reports.
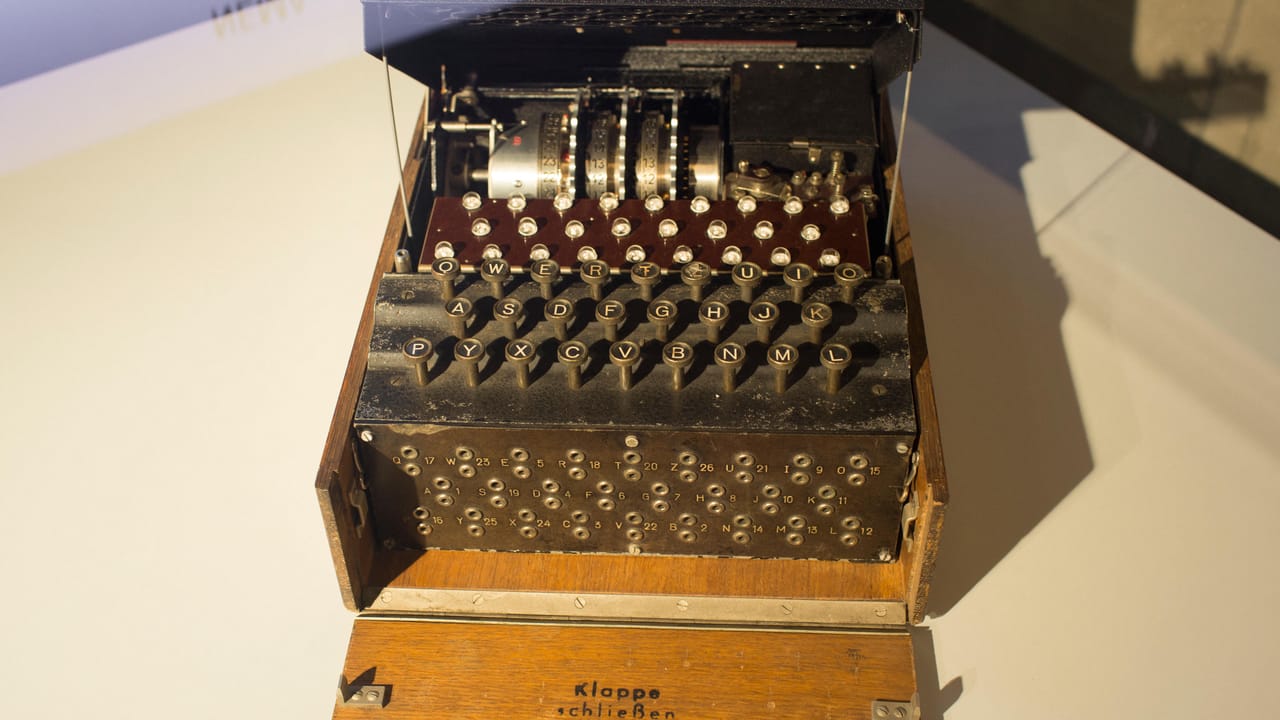
Operational Resilience: Cryptographic Lessons from the Enigma Device
An analysis of historical cryptographic failures within the Enigma machine and how these resilience errors inform modern cybersecurity defense strategies.

MuddyWater Deploys BugSleep Backdoor in Targeted Regional Campaigns
Iranian state actor MuddyWater introduces the custom BugSleep backdoor, targeting Middle Eastern and African entities using spear-phishing and RMM abuse.