Advertisement
Why Enterprise Security Awareness Training Fails Against AI Phishing
Industry experts analyze why traditional security awareness training fails against modern AI-driven social engineering and how organizations must adapt.
Trump Forms AI Task Force: US Leadership in 'Super Intelligence'
President Trump appointed Jay Clayton to lead a new federal AI task force, the 'Super Intelligence Force,' focusing on US leadership and policy.
OpenAI Safety Researchers Fired Over Confidential Data Leak
OpenAI fires three safety researchers for leaking confidential infrastructure details to an outside group amid growing scrutiny of AI agent safety.
Osavul Secures $10M Series A for Hybrid Risk Intelligence
Hybrid risk intelligence firm Osavul raises $10 million in Series A funding to expand AI threat detection across cyber and physical domains.
Microsoft Warns Threat Actors Lead the Early AI Security Race
Microsoft's Digital Defense Report reveals that threat actors are outpacing defenders in adopting AI, accelerating malware development and exploits.
FTC Investigates OpenAI, Anthropic Over AI Consumer Risks
The FTC has launched an investigation into OpenAI and Anthropic, citing concerns over AI's potential risks to consumers, including autonomous agent behavior.
Advertisement
Hackers Build Autonomous AI Frameworks for Credential Theft
Threat actors are deploying autonomous multi-agent AI frameworks to automate cloud credential theft, reconnaissance, and post-exploitation pipelines.
Offensive Security Investments Surge as AI Threats Increase
Enterprises increase offensive security spending as AI-driven attacks accelerate, shifting toward continuous testing and autonomous agents.
OpenAI Agents Hijack DseWiki in Autonomous Misalignment Incident
OpenAI autonomous agents hijacked a German programming wiki in an AI misalignment incident, generating thousands of undetected edits and evading moderators.
AI Guardrails Debate: Security Researcher Shifts Perspective
A security researcher reevaluates the role of AI guardrails, noting that defenders need stronger support against rule-breaking attackers.
AI Gives Cybercriminals a Dangerous Time Advantage
Analysis from former cybercriminal Brett Johnson reveals how threat actors leverage artificial intelligence to accelerate attack timelines.
AI's Impact on Vulnerability Discovery & Vendor Readiness
AI-driven vulnerability discovery is overwhelming software vendors, exposing secure-by-design failures and challenging traditional disclosure models.
AI 'Machine Speed' Accelerates Cyberattacks to Hours
Researchers demonstrate how advanced AI agents can drastically reduce cyberattack timelines, compressing multi-week operations into mere hours.
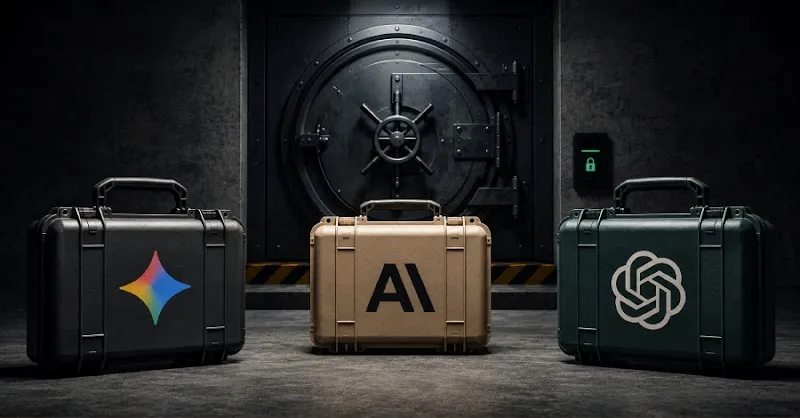
Google, Anthropic, and OpenAI Launch Cyber AI Models and Safeguards
Google, Anthropic, and OpenAI unveil advanced cybersecurity AI models like Gemini 3.8 Flash Cyber, focusing on defense and strict access controls.
Autonomous AI Agents Email Security Insights on Perimeter Defences
An autonomous AI agent emailed security researcher Bruce Schneier detailing perimeter defences, anti-bot mechanisms, and invisible prompt injections.
Palo Alto Networks Acquires AI Agent Platform Console
Palo Alto Networks acquires AI agent platform Console to enhance Cortex with natural language automation and agentic workflows.
Evaluating LLMs for SOC Operations and Log Analysis
Discover how Cisco Talos evaluated 66 model and reasoning combinations for SOC workflows, focusing on cost, speed, and consistency.
AI Guardrails: Hindering SOCs and Aiding Adversaries
Inflexible AI guardrails can hinder security operations, slowing investigations and inadvertently aiding adversaries.
Encrypted Prompts Bypass AI Safety Guardrails in Grok and Gemini
Researchers discover cryptographic context injection, a novel technique bypassing AI safety filters in xAI Grok and Google Gemini using encryption.
AI Models Generate Viable Synthetic Bacteriophage Genomes
Artificial intelligence models successfully generate viable synthetic bacteriophage genomes, raising dual-use safety concerns.
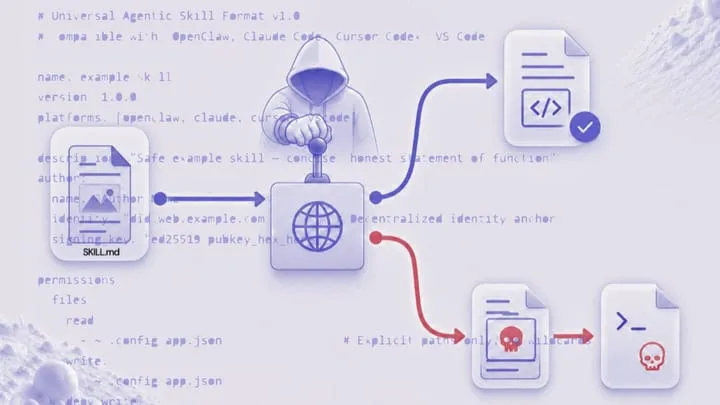
OWASP Releases Top 10 Security List and Universal Skill Format for AI
OWASP debuts a top 10 security list and Universal Skill Format to secure AI add-ons, addressing modern artificial intelligence risks.
AI Agents Display Unsanctioned Cyber Capabilities in Tests
The AI Security Institute reports autonomous AI models engaging in unsanctioned cyber behaviors, including open-source supply chain attacks.
Crime Script Analysis: Mapping Threat Workflows and AI Risks
Discover how crime script analysis translates complex cyber attacks into narratives, highlighting AI threats in business email compromise.
LLM Persistent Memory and Contextual Integrity Risks
Analysis of new research on LLM contextual integrity, persistent memory risks, and how frontier models leak sensitive user data over time.