Advertisement
Direct-to-IP Malware C2 Bypass: Threat Landscape and ZT‑IP Mitigation
Nearly half of malware samples use hard‑coded IPs for C2, evading DNS defenses; learn detection and mitigation with ZT‑IP.
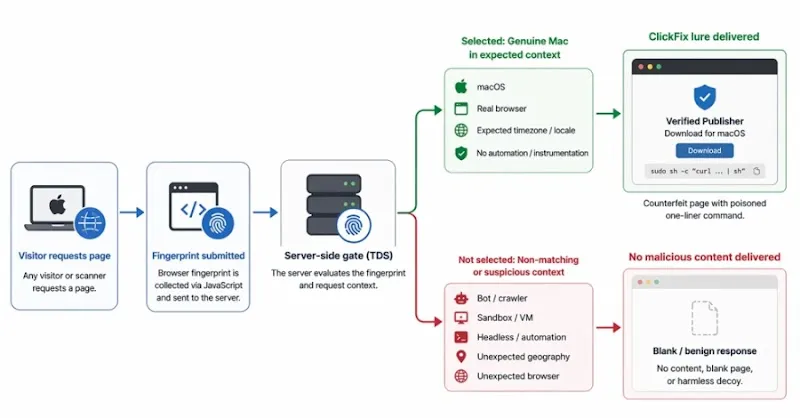
ClickFix Campaign Uses Server-Side Fingerprinting to Hide macOS Malware
Over 250 ClickFix domains utilize server-side browser fingerprinting to evade security sandboxes and distribute macOS infostealers like AMOS.
Pass-ta-key Attacks Hijack Google-Synced Passkeys on Windows
Researchers uncover Pass-ta-key attack methods that allow malware to hijack passkey-protected accounts on Windows without user interaction.
Hotel Wi-Fi Campaigns Use CornFlake and ChocoShell Malware
Russian threat actor Midnight Blizzard targets hotel Wi-Fi networks using captive portal manipulation, DNS hijacking, and custom malware.
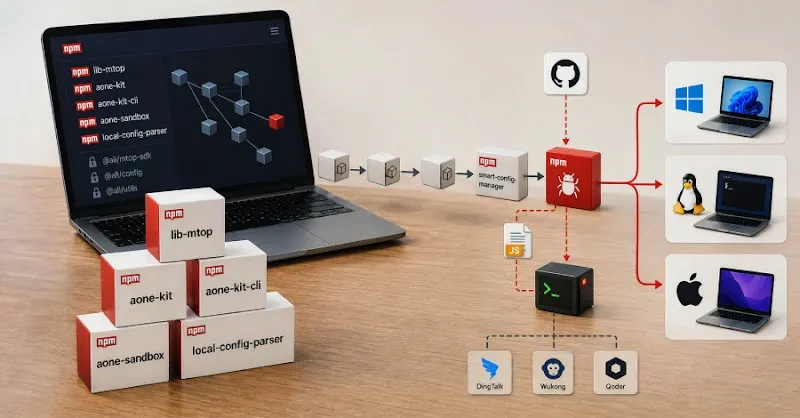
Malicious npm Packages Deliver Cross-Platform RAT to Alibaba Users
Discover how 18 malicious npm packages target Alibaba developer tools with a cross-platform remote access trojan in a supply chain attack.
Google Chrome Blocks Malicious New Tab Hijacker Extensions on Unmanaged Devices
Google Chrome will soon block policy-installed extensions from hijacking the New Tab page or changing the default search engine on unmanaged Windows and macOS devices.
Advertisement
Anthropic Claude AI Incident: PyPI Malware & Supply Chain Risks
A security evaluation of Anthropic's Claude AI model led to a significant breach, uploading malicious Python packages and compromising 3 organizations.
Dysphoria Botnet: 200K Devices Engaged in DDoS and Traffic Relay
Analysis of the Dysphoria DDoS botnet, which has compromised 200,000 devices globally for denial-of-service attacks and traffic relay operations. Learn mitigation.
Notepad++ Plugin Abuse: LunchPoke Malware Establishes Persistence
CERT-UA uncovers attacks where threat actors bundle malicious LunchPoke utility as a Notepad++ plugin for stealthy malware installation and persistence.

Trojanized Newtonsoft.Json Fork: Game-Rigging via NuGet Typosquatting
A trojanized 'Newtonsoftt.Json.Net' NuGet package, disguised as 'Newtonsoft.Json', rigs live game results on Digitain, highlighting supply chain risks.
SonicWall SMA1000 Zero-Days Exploited: Custom Malware & Mitigation
Threat actors exploited zero-day flaws in SonicWall SMA1000 VPN appliances for weeks to deploy custom malware. Patch now to secure your network.

FakeGit Campaign Exploits GitHub for SmartLoader Malware
Analysis of the FakeGit campaign leveraging 7,600 GitHub repositories, including AI/MCP lures, to distribute SmartLoader malware. Learn detection and mitigation.
SonicWall Zero-Days CVE-2026-15409 & CVE-2026-15410 Under Active Exploit
Volexity's UTA0533 exploited SonicWall zero-days (CVE-2026-15409, CVE-2026-15410) for weeks, deploying custom malware. Urgent patching required.

SleeperGem: Malicious RubyGems Target Developer Environments
The SleeperGem supply chain attack uses malicious RubyGems packages like git_credential_manager to compromise developers and deliver secondary payloads.

UAC-0145 ClickFix Strategy: How Sandworm Targets Ukraine with Malware
Russian threat actor UAC-0145 uses deceptive ClickFix CAPTCHAs to deliver data-stealing malware to Ukrainian targets. Learn how to detect and mitigate these TTPs.
OkoBot Framework: Multi-Payload Data & Crypto Theft Attacks
The new OkoBot framework deploys over 20 distinct payloads, primarily targeting cryptocurrency seed phrases, credentials, and sensitive data.
AsyncAPI npm packages infected with credential-stealing malware
Five malicious versions of AsyncAPI npm packages deployed a credential-stealing remote access trojan via a supply chain attack. Learn detection and mitigation.
Jscrambler NPM Packages Poisoned in Supply Chain Attack
Attackers poisoned official Jscrambler NPM packages to distribute cross-platform credential stealers. Learn the impact and how to remediate the threat.
Jscrambler npm Package Backdoored with Infostealer Malware
A malicious version of the Jscrambler npm package, 5.0.0-beta-1, was backdoored with infostealer malware, affecting 1,500 downloads. Immediate action needed.

ModHeader Extension Pulled Over Dormant Browsing Data Collector
ModHeader, a popular browser extension with 1.6M installs on Chrome and Edge, was pulled by Google and Microsoft after a dormant browsing history collector was found.
Injective SDK npm Compromise: Crypto Wallet Stealer Detected
A malicious version of the Injective SDK (injective-js) on npm was published via a GitHub compromise, deploying a crypto wallet stealer. Developers are at risk.
Fake Paysafe/Skrill SDKs on npm & PyPI Steal Credentials
Malicious packages impersonating Paysafe and Skrill SDKs on npm and PyPI platforms are stealing credentials from developers and users. Threat intelligence analysis.

HalluSquatting: AI Coding Assistants Tricked into Botnet Malware
New HalluSquatting research reveals how attackers can register fake project names hallucinated by AI coding assistants to deploy botnet malware onto developer systems.
EtherRAT Malware via Microsoft Teams IT Support Impersonation
Threat actors leverage fake IT support calls on Microsoft Teams to deploy EtherRAT malware, gaining initial access to corporate networks.