Advertisement
CVE-2016-3081: Apache Struts RCE via Command Injection — Patch Now
CISA confirms active exploitation of CVE-2016-3081, an Apache Struts command injection flaw leading to remote code execution.
Multi-Vendor Patches: Adobe, Apple, Foxit, Microsoft Vulnerabilities
Cisco Talos discloses patched privilege escalation, RCE, and information disclosure vulnerabilities across Adobe, Apple, Foxit, and Microsoft products.
LibreOffice & OpenOffice RCE via Malicious Spreadsheets
Vulnerabilities in LibreOffice (CVE-2026-63277) and Apache OpenOffice (CVE-2026-59265) allow RCE via malicious spreadsheets without macro warnings.
Dell CSM Critical Flaws: Unauthenticated Admin on Kubernetes Nodes
Dell Container Storage Modules (CSM) versions prior to 1.17.0 are critically vulnerable, enabling unauthenticated admin access and Kubernetes node compromise.
CVE-2026-102489: Zammad Session Fixation Leads to RCE – Patch Now
CISA confirms active exploitation of CVE-2026-102489 in Zammad, a session fixation vulnerability enabling remote code execution.
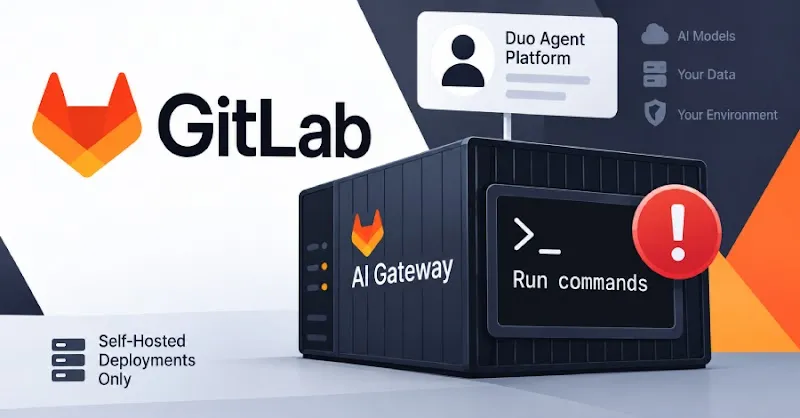
CVE-2026-90970: GitLab AI Gateway RCE Flaw — Update Self-Hosted Now
GitLab patched a critical AI Gateway flaw (CVE-2026-90970). Logged-in Duo Agent users can achieve remote command execution on self-hosted instances. Update immediately.
Advertisement
Microsoft Patch Tuesday: Zero-Days & Critical RCEs Addressed
Microsoft's record-breaking Patch Tuesday fixes 974 vulnerabilities, including actively exploited zero-days and critical RCEs in Windows.
AI's Impact on Vulnerability Discovery & Exploitation Trends
Google Threat Intelligence reports AI is doubling vulnerability disclosures and exploitation, shifting focus to more consequential flaws including RCEs.
CVE-2026-73570: Unauthenticated RCE in Zimbra ZCS Exploited
Threat actors are actively exploiting CVE-2026-73570, an unauthenticated RCE flaw in Zimbra Collaboration Suite, to deploy web shells and exfiltrate sensitive data.
N-able N-central RCE via CVE-2026-86218 Under Active Exploitation
CISA confirms active exploitation of CVE-2026-86218, a pre-authentication remote code execution flaw in N-able N-central, urging immediate mitigation.
MikroTik RouterOS Critical Flaws Chained to Hack Routers
Critical vulnerabilities in MikroTik RouterOS, including CVE-2026-67276 and CVE-2026-86060, are actively exploited to gain full control of routers. Patch immediately.
MikroTik RouterOS Unauthenticated SSH Exploit: Critical Advisory
Attackers are exploiting a critical vulnerability in MikroTik RouterOS via internet-exposed SSH to gain full administrative control without authentication.
CVE-2026-6471: PostgreSQL Takeover via Logical Decoding Flaw
CVE-2026-6471, a 12-year-old PostgreSQL vulnerability, allows attackers with low replication privileges to achieve RCE and full database server takeover.
CVE-2026-73749: HPE ArubaOS-CX RCE Flaw Patched
HPE patches a critical remote code execution flaw, CVE-2026-73749, in ArubaOS-CX switches. Unauthenticated attackers can exploit a buffer overflow.
Critical Cisco Nexus 9000 RCE (CVE-2026-20212) & IOS XR Hardening
Cisco addresses a critical RCE flaw (CVE-2026-20212) in Nexus 9000 switches, alongside significant IOS XR hardening updates.
CVE-2026-9586: Sangoma Switchvox RCE via SQL Injection
Sangoma Switchvox is affected by CVE-2026-9586, an unauthenticated remote SQL injection vulnerability enabling RCE, with active exploitation confirmed.
CVE-2026-49869: Kestra OSS OS Command Injection Exploited
CISA has added CVE-2026-49869, an OS command injection in Kestra OSS, to its KEV catalog, confirming active exploitation by unauthenticated attackers.
CVE-2021-23758: Ajax.NET RCE via Deserialization of Untrusted Data
CVE-2021-23758 in Ajax.NET Professional allows remote code execution via untrusted data deserialization, with CISA confirming active exploitation.
CVE-2026-60004: Gitea Code Injection Under Active Exploitation
CISA confirms active exploitation of CVE-2026-60004, a Gitea code injection vulnerability allowing shell command execution with repository write access.
Microsoft Entra ID RCE Flaw CVE-2026-69836 Fully Mitigated
Microsoft has fully mitigated a critical remote code execution flaw, CVE-2026-69836, in Entra ID (formerly Azure AD). No customer action is required.
CVE-2026-72529: Critical RCE in TrueConf Server via Missing Auth
CISA warns of active exploitation of CVE-2026-72529 in TrueConf Server, allowing remote attackers to execute arbitrary scripts via port 4307/TCP.
CVE-2026-72530: TrueConf Server Remote Code Execution
CISA confirms active exploitation of CVE-2026-72530, a TrueConf Server code injection flaw leading to remote code execution. Immediate patching is critical.
Zimbra CVE-2026-73570 Actively Exploited: Patch Now
Active exploitation targets Zimbra servers via CVE-2026-73570, a high-severity flaw allowing unauthenticated RCE. Patch to v10.1.20 now.
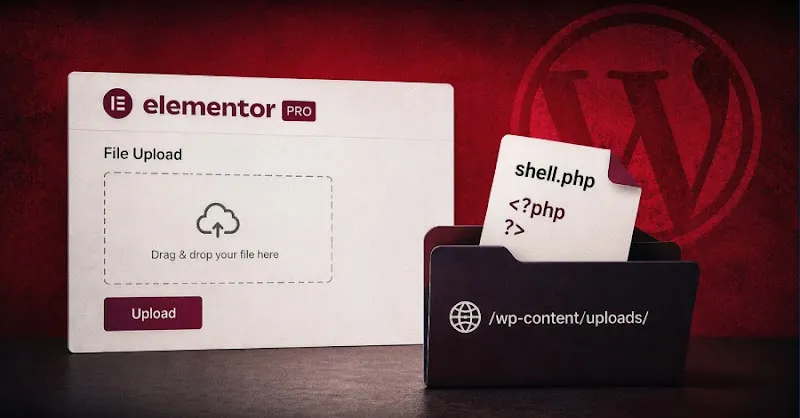
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.