Advertisement
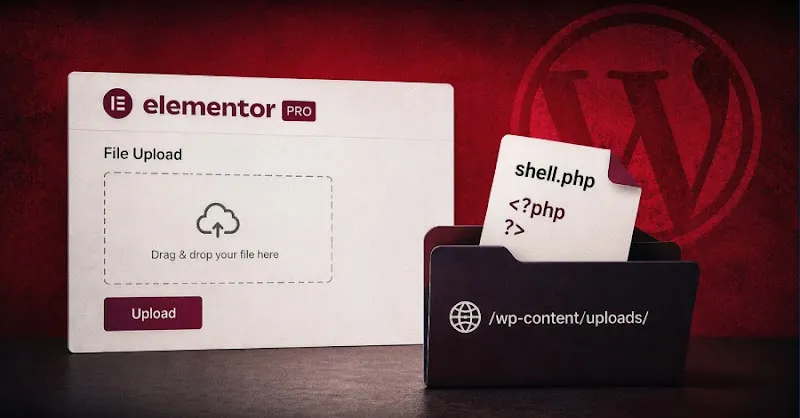
CVE-2026-32475: Elementor Pro Unauthenticated RCE Flaw
A critical flaw, CVE-2026-32475, in Elementor Pro allows unauthenticated attackers to upload PHP files and execute code, affecting versions <= 4.2.1.
CVE-2026-33824: Microsoft IKE Double Free RCE Exploit
CISA confirms active exploitation of CVE-2026-33824 in Microsoft Internet Key Exchange (IKE) Service Extensions, enabling remote code execution.
Unisoc Modem Exploit Chain: Android Takeover via Video Call
An exploit chain targeting Unisoc modems allows remote Android device takeover through a malicious video call, requiring victim interaction.
CVE-2025-62593: Ray-Project Ray RCE Exploited In Wild
CISA confirms active exploitation of CVE-2025-62593, a critical code injection vulnerability in Ray-Project Ray allowing remote code execution. Developers are targeted.
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.
CVE-2026-72898: Metabase SQL Injection Active Exploitation
CISA adds Metabase CVE-2026-72898 SQL injection to its KEV catalog, enabling unauthenticated remote attackers to gain admin access.
Advertisement
CVE-2026-63077: JetBrains TeamCity RCE via Deserialization
CISA adds CVE-2026-63077 to KEV, indicating active exploitation of a JetBrains TeamCity deserialization RCE vulnerability.
Metabase Zero-Day SQL Vulnerability Threatens Analytics Platforms
Unpatched Metabase business-analytics zero-day vulnerability allows remote administrative access and threatens downstream corporate networks.
CVE-2026-53413: Zoom Zero-Click RCE – Patch Now
Zoom patches CVE-2026-53413, a critical zero-click RCE in its annotator function, affecting all clients. Immediate patching is advised.
Pixel 9 Zero-Click RCE: Exploiting Dolby Unified Decoder
Project Zero details a zero-click exploit chain targeting Google Pixel 9 via the Dolby Unified Decoder, leading to arbitrary code execution.
Bendix EC80 Hidden RCE and DoS Flaws in Brake Controllers
NMFTA reveals Bendix EC80 heavy-truck brake controllers fixed critical, wirelessly reachable remote code execution and DoS flaws in a safety recall.
CVE-2026-8037: Progress LoadMaster Command Injection RCE
Progress LoadMaster command injection (CVE-2026-8037) allows unauthenticated attackers to execute arbitrary commands. Active exploitation confirmed by CISA.
Google ADK for Python RCE: Agent-to-Agent Attacks Expose Secrets
Pillar Security uncovered agent-to-agent RCE flaws in Google's ADK for Python, allowing secret exposure and PR tampering, risking supply chain integrity.
CVE-2026-50522: SharePoint RCE via Deserialization — Patch Now
CISA confirmed active exploitation of CVE-2026-50522 in Microsoft SharePoint. Attackers leverage a deserialization vulnerability to execute code remotely. Patch…
VMware Critical Flaws: Auth Bypass, RCE, VM Escapes Patched
VMware has patched critical vulnerabilities across vCenter, ESX, Workstation, and Fusion, addressing authentication bypass, remote code execution, and VM escapes.
CVE-2024-24691: Zoom Windows Client Account Takeover - Patch Now
Zoom has addressed CVE-2024-24691, a critical 9.6 CVSS vulnerability in Windows clients allowing unauthenticated account takeover. Learn how to patch and defend.

CVE-2026-45659: SharePoint RCE Exploitation - Mitigation Guide
CISA adds CVE-2026-45659, a high-severity SharePoint Server deserialization flaw, to KEV catalog after confirmed active exploitation by threat actors.
CryptoBandits Malware: Tor-Abusing Backdoor & Data Theft
CryptoBandits malware functions as a backdoor, leveraging Tor and a SOCKS5 proxy for stealthy data theft and remote code execution capabilities.
Gogs RCE via CVE-2024-39930 — Mitigation and Patch Guide
A critical argument injection in Gogs (CVE-2024-39930) allows authenticated users to achieve RCE via malicious pull requests. Learn how to patch and defend.

Gogs Authenticated RCE: Arbitrary Code Execution - Mitigation Guide
A critical RCE vulnerability in Gogs allows authenticated users to execute arbitrary code. Runtime Rebel provides an analysis and urgent mitigation guidance.
Exim RCE: Unauthenticated Remote Code Execution Critical Flaw
A new critical flaw in Exim mailer allows unauthenticated remote code execution on certain configurations. Immediate patching is vital for security professionals.
cPanel CVE-2026-41940 Exploitation: 40,000 Servers Compromised
Attackers leverage a zero-day vulnerability in cPanel, identified as CVE-2026-41940, to gain administrative access to over 40,000 hosting servers.
CVE-2024-36985: Splunk Enterprise RCE via File Upload - Patch Guide
Splunk patches a high-severity RCE vulnerability (CVE-2024-36985) allowing low-privileged users to execute code on Windows-based Enterprise instances.

Adobe Reader Zero-Day Exploited via Malicious PDF Documents
Researchers reveal a sophisticated Adobe Reader zero-day exploit used in the wild since late 2025, involving malicious PDF invoices to compromise systems.