Advertisement
Microsoft AI Report Overlooks Government Attacks via Own Bugs
Microsoft's latest AI cyber risk report overlooks critical details about threat actors exploiting Microsoft vulnerabilities to target government agencies.
Microsoft Patch Tuesday: 1,400+ Flaws, One Zero-Day
Microsoft patched over 1,400 security flaws, including one Windows Shell zero-day (CVE-2026-96951) and 78 critical RCE vulnerabilities.
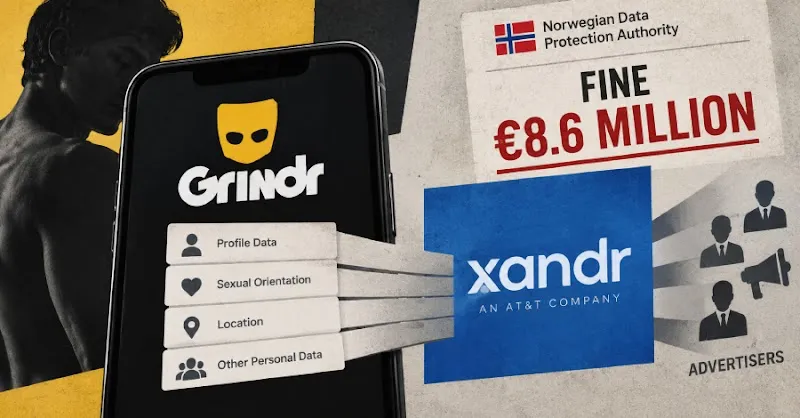
Xandr Fined Record €8.6M for Relaying Grindr Data
Norwegian DPA fines Microsoft-owned Xandr a record €8.6 million for illegally relaying Grindr users' sensitive sexual orientation data.
Multi-Vendor Patches: Adobe, Apple, Foxit, Microsoft Vulnerabilities
Cisco Talos discloses patched privilege escalation, RCE, and information disclosure vulnerabilities across Adobe, Apple, Foxit, and Microsoft products.
CVE-2026-96940: Exchange Server Auth Flaw Exposes Mailboxes
Microsoft addresses a high-severity flaw, CVE-2026-96940, in on-premises Exchange Server allowing authenticated attackers to read mailboxes.
Microsoft X Account Hijacked by Crypto Scammers
Microsoft's official X account was compromised, used to promote a Clippy-themed cryptocurrency scam. Investigate potential account takeover methods.
Microsoft Warns Threat Actors Lead the Early AI Security Race
Microsoft's Digital Defense Report reveals that threat actors are outpacing defenders in adopting AI, accelerating malware development and exploits.
Microsoft Patch Tuesday: Zero-Days & Critical RCEs Addressed
Microsoft's record-breaking Patch Tuesday fixes 974 vulnerabilities, including actively exploited zero-days and critical RCEs in Windows.
CVE-2026-65660: Microsoft SharePoint Code Injection Exploit
CISA adds CVE-2026-65660 to its Known Exploited Vulnerabilities catalog after confirming active exploitation against Microsoft SharePoint.
CVE-2026-66804: Windows Dangling COM Object Privilege Escalation
Microsoft fixed CVE-2026-66804, a privilege escalation bug in Windows, due to a dangling COM object registration.
CVE-2026-85880: Windows ALPC Heap Overflow Exploited
CISA confirms active exploitation of CVE-2026-85880, a heap-based buffer overflow in Microsoft Windows ALPC leading to local privilege escalation.
Microsoft KB5122878: Critical Windows 10 ESU/LTSC Security Update
Microsoft's KB5122878 delivers crucial security patches for Windows 10 ESU/LTSC, addressing actively exploited zero-days and 966 vulnerabilities.
BigBear PhaaS Bypasses Microsoft 365 MFA at 258 Orgs
BigBear 2.0 PhaaS uses Evilginx2 AiTM to bypass Microsoft 365 MFA, stealing credentials and session cookies from 258 organizations.
Microsoft 365 Vishing Leads to Executive Data Theft, Extortion
A widespread threat cluster, PREY-0058, targets Microsoft 365 executives with vishing, AitM token theft, and data extortion.
Microsoft Teams Abuse, The Gentlemen Ransomware, and PhaaS Trends
Analysis of social engineering campaigns via Microsoft Teams, The Gentlemen ransomware operations, and emerging phishing-as-a-service kits.
Silver Fox Malware Campaign Impersonates Software Vendors
An active Silver Fox malware campaign uses fake software download sites to disable Windows Update and weaken Microsoft Defender defenses.
Microsoft Defender Blocks Legitimate Google Search Links
Microsoft Defender for Office 365's Safe Links feature is incorrectly flagging legitimate Google search results as malicious, blocking user access and generating alerts.
CVE-2026-62911: Exchange Servers Vulnerable to Mailbox Hijack
Nearly 22,000 Microsoft Exchange Servers remain unpatched against CVE-2026-62911, an auth bypass allowing mailbox hijack attacks.
Spring Ring Voice Phishing Targets Microsoft Teams Users
Spring Ring is an ongoing vishing campaign leveraging external Microsoft Teams accounts to impersonate IT support for payload delivery and NTLM relay attacks.
Mabna Institute Espionage, BTR.sys Kernel Bypass, & Malware
Runtime Rebel details state-sponsored espionage by Mabna Institute, a kernel-level bypass using Microsoft Defender's BTR.sys, and new malware campaigns.
Microsoft Entra ID RCE Flaw CVE-2026-69836 Fully Mitigated
Microsoft has fully mitigated a critical remote code execution flaw, CVE-2026-69836, in Entra ID (formerly Azure AD). No customer action is required.
Weaponizing Defender's BTR.sys to Disable Security Software
Attackers can weaponize a legitimate Microsoft Defender driver to delete security software at boot, impacting Windows 7-11.
SynkLoader Malware Steals Credentials in Microsoft Teams Phishing
New SynkLoader malware distributed via Microsoft Teams phishing campaigns uses a fake lock screen to steal Windows credentials, enabling corporate network access.
Entra Log Analysis: Detecting Password Spray Attacks with PowerShell
Learn to analyze Microsoft Entra sign-in logs using PowerShell to detect password spray attacks and anomalous successful logins from unexpected geographic locations.