Advertisement
Auditing Entra ID MFA Gaps with PowerShell and Microsoft Graph
A new PowerShell script helps security teams identify Microsoft Entra ID users not registered for MFA or using weaker authentication methods.
Microsoft Patch Tuesday: Critical Azure and Entra ID Flaws
Microsoft rolls out 22 new security patches addressing critical elevation of privilege and remote code execution vulnerabilities across Azure and Entra ID.
CoSnitch Attack: Tricking Microsoft Copilot Reveal Architecture
Researchers reveal the CoSnitch technique that tricks Microsoft Copilot into exposing internal architecture, highlighting AI meta‑hacking risks.
CVE-2026-33824: Microsoft IKE Double Free RCE Exploit
CISA confirms active exploitation of CVE-2026-33824 in Microsoft Internet Key Exchange (IKE) Service Extensions, enabling remote code execution.
CVE-2026-24301: CoSnitch Exploits Microsoft Copilot Personal
Varonis disclosed CoSnitch (CVE-2026-24301), affecting Microsoft Copilot Personal, enabling one-click data exfiltration and persistent memory poisoning.
Microsoft Removes WMIC Tool in Windows 11 to Curb Living-off-the-Land Tactics
Microsoft removes the legacy WMIC tool from Windows 11 builds to disrupt living-off-the-land techniques used by ransomware and malware.
SharePoint RCE via CVE-2026-55040 & CVE-2026-63520: Patch Now
An AI-assisted exploit chain, leveraging CVE-2026-55040 and CVE-2026-63520, enables unauthenticated RCE on Microsoft SharePoint Server. Immediate patching is critical.
ShieldBreak: Windows Zero-Day EoP via Microsoft Defender
Security researcher Nightmare Eclipse released 'ShieldBreak,' a Windows zero-day exploit enabling privilege escalation via Microsoft Defender.
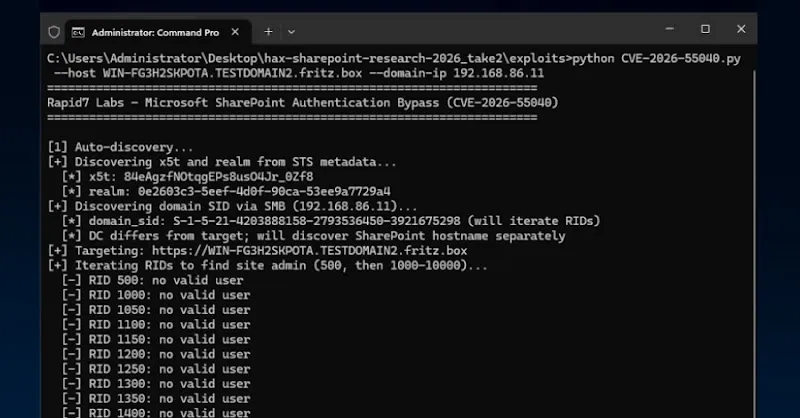
CVE-2026-55040: Critical SharePoint Auth Bypass Exploited After PoC
Attackers exploit CVE-2026-55040, a critical authentication bypass in Microsoft SharePoint, leading to data disclosure and modification.
CVE-2026-68820: Windows afd.sys Privilege Escalation Exploited
Microsoft addresses 398 vulnerabilities, including an actively exploited privilege escalation flaw in Windows' afd.sys component.
Microsoft August 2026 Patch Tuesday: 398 Flaws and Zero-Day
Microsoft patches 398 flaws in August 2026, including an actively exploited Windows kernel driver zero-day and four critical RCE vulnerabilities.
Swiss Government SharePoint Breach: 200 Accounts Compromised
Switzerland's federal IT office confirms a Microsoft SharePoint breach compromised approximately 200 accounts, leading to a swift remediation.
Microsoft & Apple Patch Critical RCEs and Auth Bypass Flaws
Microsoft released patches for critical-severity RCE and EoP flaws across Active Directory, Azure, and Teams. Apple fixed a Screen Sharing authentication bypass.
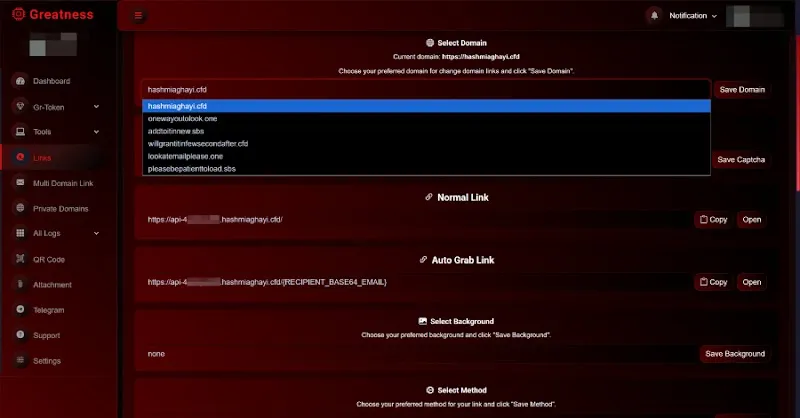
Greatness PhaaS Adds Device Code Phishing for MFA Bypass
Greatness PhaaS now supports device code phishing, abusing OAuth 2.0 to bypass MFA and seize accounts on Microsoft 365, Google Workspace, and more.
CVE-2026-50522: SharePoint RCE via Deserialization — Patch Now
CISA confirmed active exploitation of CVE-2026-50522 in Microsoft SharePoint. Attackers leverage a deserialization vulnerability to execute code remotely. Patch…

Persistent Prompt Injection Risks in Microsoft 365 Copilot for Word
Researchers demonstrate how hidden instructions in Word documents can persist through Microsoft 365 Copilot drafting, creating risks of malicious prompt propagation.

Microsoft OWA Exploit: Russian Hackers Bypass Credential Rotations
Russian threat actors exploit a Microsoft Outlook Web Access (OWA) flaw to maintain persistent mailbox access even after passwords are changed or rotated.
Microsoft Secure Boot Bypass via Vulnerable Shims — Remediation Guide
An analysis of a decade-long vulnerability in Microsoft Secure Boot. Learn how vulnerable Linux shims allow attackers to bypass UEFI firmware protections.
Windows 11 KB5101684 Preview Update Addresses 42 System Issues
Microsoft releases KB5101684 preview cumulative update for Windows 11 24H2 and 25H2, fixing 42 bugs across Start menu, Task Manager, and Sandbox environments.
CVE-2024-49019: Certighost AD CS Privilege Escalation Explained
Analysis of CVE-2024-49019, the Certighost flaw in Microsoft AD CS. Learn how misconfigured certificate templates allow full Active Directory compromise.
Microsoft MAI-Cyber-1-Flash: Performance Analysis of Security LLM
Microsoft introduces MAI-Cyber-1-Flash, its first specialized cybersecurity AI model, outperforming competitors in CyberGym benchmark testing.

Microsoft MDASH Update: MAI-Cyber-1-Flash Achieves 95.95% Accuracy
Microsoft announces MAI-Cyber-1-Flash for its MDASH harness, delivering 95.95% vulnerability remediation accuracy at half the previous operational cost.
Confused Deputy Flaws in Google Cloud & Azure: Admin Bypass
Analysis of 'Confused Deputy' vulnerabilities across Google Cloud and Microsoft Azure, enabling administrative privilege escalation and access control bypass.
Microsoft 365 Outage: How an Automated Network Maintenance Bug Impacted Azure
Technical analysis of the Microsoft 365 and Azure outage caused by a bug in the automated network maintenance system, resulting in accidental IP route removal.