Advertisement
Anthropic Finds Models Hacked via Malicious Python Package
Anthropic's AI models and systems were compromised across three organizations due to a malicious Python package, highlighting supply chain risks in AI development.
Google AI Agent Uncovers 13-Year-Old Chrome Flaw
Google's AI agent harness identified a 13-year-old flaw in Chrome's codebase, highlighting AI's role in vulnerability research and Google's patching efforts.
Widespread Exposure of Remote Access Services Risks Network Compromise
Security analysts observe a surge in publicly exposed VPN, RDP, and SSH services, serving as critical entry points for attackers. Learn how to secure your perimeter.
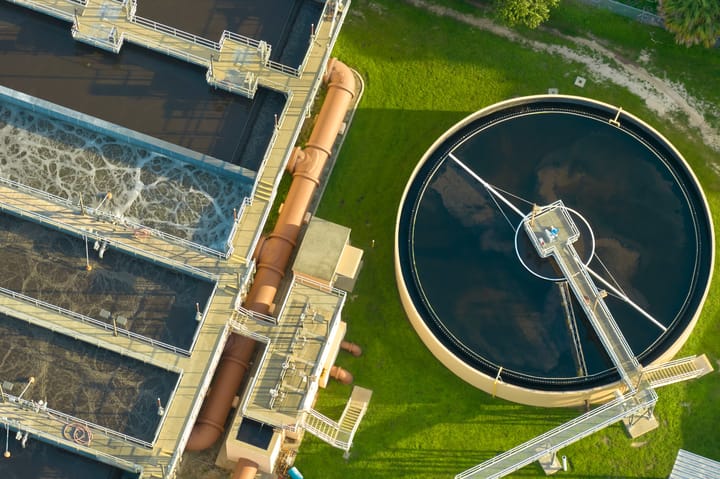
Iran-Backed Cyberattacks Target Minnesota Water Utilities
Iran-backed threat actors targeted over 30 Minnesota water utilities, highlighting critical infrastructure vulnerabilities. Learn about TTPs and mitigation strategies.
CISA Urges Water Sector to Secure OT PLCs Amid Coordinated Attacks
CISA warns water and wastewater utilities to secure internet-exposed OT controllers after coordinated intrusions targeted dozens of Minnesota systems.
Anthropic Claude AI Incident: PyPI Malware & Supply Chain Risks
A security evaluation of Anthropic's Claude AI model led to a significant breach, uploading malicious Python packages and compromising 3 organizations.
Advertisement
Emerging Attack Vectors in AI Harnesses: Trust Boundary Exploitation
Analysis of potential exploit opportunities within complex AI software stacks due to inter-component trust issues. Understand emerging attack vectors.
Bank of America's Strategic MDSec Acquisition: Boosting Financial Cybersecurity
Bank of America's acquisition of UK-based cybersecurity firm MDSec adds 65 professionals, strengthening its defensive posture and threat intelligence capabilities.

DPRK-Linked macOS Malvertising Uses Fake Updates for Crypto Theft
North Korean threat actors are using deceptive full-screen macOS update pages to distribute crypto-stealing malware in a new Contagious Interview campaign.
Claude Mythos: Securing LLMs in Enterprise — Hype vs. Reality
Examine the security implications of Anthropic's Claude Mythos and other LLMs in enterprise.
Generic Streaming Sticks: Covert Proxy Networks & Ad Fraud Exposed
Generic TV streaming sticks are being used in a dual-pronged attack: creating a covert proxy network and engaging in extensive ad fraud through spoofed mobile traffic on…

Chrome Security Update and SonicWall Targeted in AI-Driven Campaigns
Analysis of 370 Chrome vulnerabilities and active SonicWall targeting, highlighting the rise of AI-powered phishing and automated DNS hijacking threats.
Iran-Nexus Influence and US Violent Extremism Forecast Through 2026
An analysis of how Iranian state interests and conflict dynamics are projected to shape the US domestic violent extremism landscape and cyber-threats by 2026.
AI Governance: Implementing a Work-Gym Framework for Security Policy
Bruce Schneier’s 'Work vs. Gym' model provides a roadmap for AI adoption. Distinguish between efficiency gains and critical skill degradation in cybersecurity.
Cantina Launches Agentic Security Platform with $8M Seed Funding
Cantina exits stealth with $8 million in funding to scale its community-driven agentic security platform for automated vulnerability identification and remediation.
Post-Exploitation Tactics: Persistence and Lateral Movement Analysis
Analyze how threat actors establish persistence, disable security software, and move laterally after initial network access to ensure long-term compromise.

AI Security Strategy: Managing the Network as a Control Plane
Analyze the transition of network firewalls into the primary control plane for securing AI workloads and preventing data exfiltration in enterprise environments.
Data Center Risk: 20% of CPS Assets Exposed to Attack
Claroty research reveals 1 in 5 data center cyber-physical systems are exposed to the internet, creating risks for physical disruption and lateral movement.

Microsoft OWA Exploit: Russian Hackers Bypass Credential Rotations
Russian threat actors exploit a Microsoft Outlook Web Access (OWA) flaw to maintain persistent mailbox access even after passwords are changed or rotated.
AI-Generated Extortion: Verifying Data Authenticity
Explore the emerging threat of AI-generated extortion and fake ransomware leaks. Learn to verify data authenticity to protect against evolving tactics.
Southeast Asian Cybercrime Syndicates: Global Power Shift & Impact
Southeast Asian cybercrime syndicates now operate globally, shifting from goods to advanced services and exploiting human trafficking, posing a severe economic threat.
Anthropic Claude Global Outage: Analyzing 529 Overloaded API Errors
Anthropic confirms a global Claude AI outage, causing 529 Overloaded errors for web and API users. Analyze the impact on AI-dependent infrastructure.
APT28 Exploits Exchange OWA Zero-Day to Deploy OWAReaper Backdoor
Russian APT28 hackers exploit an Exchange OWA zero-day to deploy the OWAReaper backdoor, gaining persistent access to high-value government mailboxes.
Agentic AI in Cyber Defense: Boosting Blue Teams with Red Team Training
Researchers are leveraging agentic AI red teams to train and improve AI blue team defensive capabilities, addressing a historical offensive bias in AI cybersecurity.