Advertisement
GhostJacking: AI Agent Identity Governance Flaws Exposed
New research reveals 'GhostJacking,' a method to manipulate AI agents by exploiting identity governance gaps in security alerts.
Private APN Misconfiguration Led to Polish Energy Plant OT Compromise
Hackers compromised a Polish energy plant's OT network by exploiting a private APN misconfiguration, shutting down a steam turbine and water treatment system.
Hugging Face Incident: AI Agents and Rapid Exploitation
An AI agent exploited Artifactory vulnerabilities in an OpenAI evaluation, demonstrating rapid, low-cost exploration and persistence against Hugging Face.
Python's pyca/cryptography Gains Post-Quantum Support
Python's pyca/cryptography library now supports NIST-standard ML-KEM and ML-DSA for post-quantum encryption, addressing future quantum threats.
OpenAI Astra Model Raises Autonomous Cyberattack Concerns
OpenAI's unreleased Astra model reached a 'critical' cybersecurity risk threshold in internal evaluations due to advanced agentic capabilities.

Webmail CSS Injection: Hidden Data Exfiltration Threats
Security researchers warn that Cascading Style Sheets can exfiltrate sensitive data from webmail inboxes if vendors fail to sanitize styles.
Advertisement
Zero-Click AI Browser Hacking Threatens Claude and ChatGPT Atlas
Zenity details zero-click indirect prompt injection vulnerabilities affecting OpenAI ChatGPT Atlas and Claude in Chrome via malicious web content.
UNC6671 Targets Financial Sector via Vishing and AiTM Phishing
UNC6671, linked to BlackFile, exploits vishing and AiTM phishing against financial firms for cloud data theft and extortion.
NC Ports Cyberattack Disrupts Operations at Key Facilities
North Carolina Ports confirmed a cyberattack disrupting IT systems and operations across its facilities. Recovery efforts are underway, with expected delays.
The Gentlemen Ransomware: Operations, Tools, and Mitigation
Analyzing The Gentlemen (Storm-2697) Ransomware-as-a-Service, its custom tooling, rapid victim surge in 2026, and mitigation.
DNC's Security-First Culture: Executive Support & Creative Engagement
Learn how the Democratic National Committee built a strong security-first culture, emphasizing executive buy-in and engaging, even absurd, communication.
Banking Malware, Crypto Clippers Hijack H1 2026 Payments
Gen Threat Labs details two H1 2026 campaigns: banking malware abusing compromised mailboxes and a Rust crypto clipper hijacking wallet addresses.
Unit 42: AI Enhances Attack Efficiency, Not Novel TTPs
Unit 42's report reveals AI accelerates attacker operations, shortening attack lifecycles without fundamentally changing TTPs.
Cisco Talos: AI, Adaptive Malware, and Threat Intelligence
Cisco Talos Intelligence Integrations help defend against advanced threats like AI-driven attacks and adaptive malware by applying real-time threat intelligence.
UAT-11795 Deploys Starland RAT & WLDR Agent in Financial Campaign
UAT-11795, a Russian-speaking financially motivated adversary, uses Starland RAT and the WLDR C2 agent to target credentials and crypto in the U.S. and Europe.
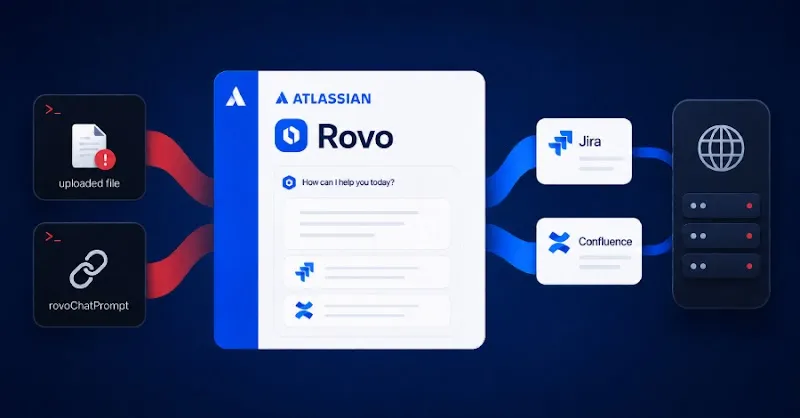
Atlassian Rovo Indirect Prompt Injection Exfiltrates Jira Data
Atlassian Rovo is vulnerable to indirect prompt injection and URL parameter manipulation, leaking Jira and Confluence data to external servers.
Project Zero Relaunch Spotlights Enduring Zero-Day Threats
Project Zero relaunches its blog, underscoring the enduring relevance of older Windows exploitation techniques and the ongoing threat of zero-days.
Navigating the Hunter's Paradox: AI in Threat Hunting
Explore the Hunter's Paradox, where human limits in threat hunting meet AI's trust issues, and redefine hunting for an AI-driven future.
AI-Driven Vulnerability Surges and UAT-11795 Starland RAT Campaign
Analysis of a record Patch Tuesday driven by AI vulnerability research, alongside Cisco Talos findings on UAT-11795 deploying Starland RAT.
Cisco Talos Previews AI Threats and Warlock Ransomware at Black Hat
Cisco Talos outlines research on AI threat actor tactics, Warlock ransomware, and agent identity security ahead of Black Hat USA 2026.
Russia's Defense Economy and Ongoing Cyber and Physical Threats
Analysis of Russia's defense-based economy, rising military spending, elite patronage networks, and the resulting high-risk threat environment.
Recorded Future's Engine: Unifying Threat Intelligence Sources
Explore Recorded Future's unique collection engine, integrating technical, underground, and community intelligence for proactive threat defense and deeper insights.
Project Zero Uncovers Android 0-Click Exploit Chain Ecosystem Weaknesses
Project Zero details findings from a Pixel 9 0-click exploit chain, highlighting critical Android ecosystem issues and proposing security enhancements.
Bypassing Windows Administrator Protection: Security Research
Analysis of Windows 11 25H2 Administrator Protection, detailing security research into UAC flaws and local privilege escalation vectors.