Advertisement
Russian Threat Clusters Target Academia and Government via Auth Abuse
Google Threat Intelligence Group tracks three Russian cyber espionage clusters abusing legitimate authentication flows and app passwords.
Transparent Tribe Targets Afghan and Indian Organizations
Pakistan-linked Transparent Tribe updates its malware toolset to target Afghan organizations and government agencies in India.
Kriminal AI Platform Fuels Cybercrime: OSINT & Social Engineering
The 'Kriminal' AI platform, offering guardrail-free social engineering and OSINT, raises significant concerns about its potential to fuel cybercrime.
Recorded Future Enhances Third-Party Risk with Unified Threat Intel
Recorded Future integrates threat intelligence and risk ratings into a unified third-party risk management platform to proactively identify vendor compromises.
SSRF Scans Target Cloud Metadata Service for Credential Access
Attackers are conducting widespread scans for Server-Side Request Forgery (SSRF) vulnerabilities to access cloud metadata services and retrieve sensitive IAM credentials.
Crime Script Analysis: Mapping Threat Workflows and AI Risks
Discover how crime script analysis translates complex cyber attacks into narratives, highlighting AI threats in business email compromise.
Advertisement
CoSnitch Attack: Tricking Microsoft Copilot Reveal Architecture
Researchers reveal the CoSnitch technique that tricks Microsoft Copilot into exposing internal architecture, highlighting AI meta‑hacking risks.
Prevalent AI Secures $22M for Data Fabric Expansion
Prevalent AI raises $22 million in growth funding to expand its AI-powered data fabric platform, focusing on US expansion and enterprise data context for security.
US Charges Iranian Hackers in $3.4B Intellectual Property Theft
US charges 17 Iranian hackers from Mabna Institute for a state-sponsored campaign stealing 31.5 TB of academic and corporate intellectual property since 2013.
SilkParasite Espionage Campaign Targets Central Asian Governments
SilkParasite espionage campaign targets Central Asian governments with seven remote access tools, including five newly documented RAT families.

AI-Driven Cyberattack Targets APAC Government Agencies
A China-linked actor reportedly deployed a near-autonomous AI framework to compromise government agencies in the APAC region, signaling a new threat landscape.
CISA Warns: Medusa Ransomware Breaches 500+ Critical Infra Orgs
CISA, FBI, and HHS alert on Medusa ransomware, which has impacted over 500 critical infrastructure organizations since June 2021, urging immediate network hardening.
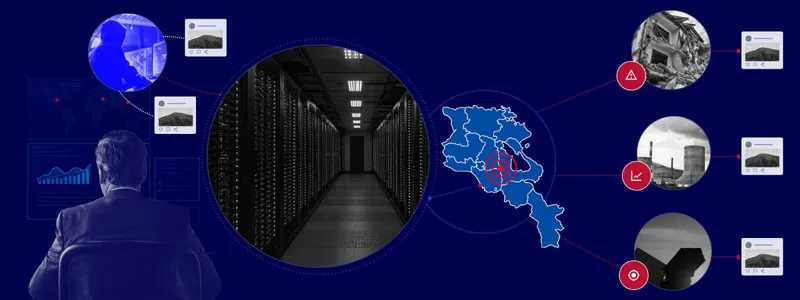
CopyCop Targets US-Armenian AI Project, Undermining Westward Shift
Russian influence network CopyCop (Storm-1516) targets the Firebird AI data center in Armenia with media impersonations to undermine US-Armenian ties.
Mitigating Large-Scale Credential Attacks and Password Spraying
Analysis of large-scale password spraying and credential theft campaigns targeting enterprise identity perimeters, edge devices, and cloud tenants.
PurpleDelta: North Korean IT Workers Exploit Remote Hiring
Recorded Future exposes PurpleDelta, North Korean IT workers using sophisticated fraudulent employment, AI, and extensive vetting evasion to fund DPRK military programs.
Agentic Source Code Review: Scaling Vulnerability Discovery with AI
Learn how Google Mandiant uses the Agentic Vulnerability Discovery Harness to accelerate secure code review and find critical flaws at scale.
LLM Persistent Memory and Contextual Integrity Risks
Analysis of new research on LLM contextual integrity, persistent memory risks, and how frontier models leak sensitive user data over time.
Ransom Busters Ransomware Affiliate Poses as Recovery Firm
A ransomware affiliate masquerades as an incident recovery service to intercept victims, divert negotiations, and manipulate ransom payments.
Nico Waisman: Evolution of Offensive Security and Open Source
Explore Nico Waisman's journey from self-taught hacker to pioneering offensive security and leading open source supply chain efforts.
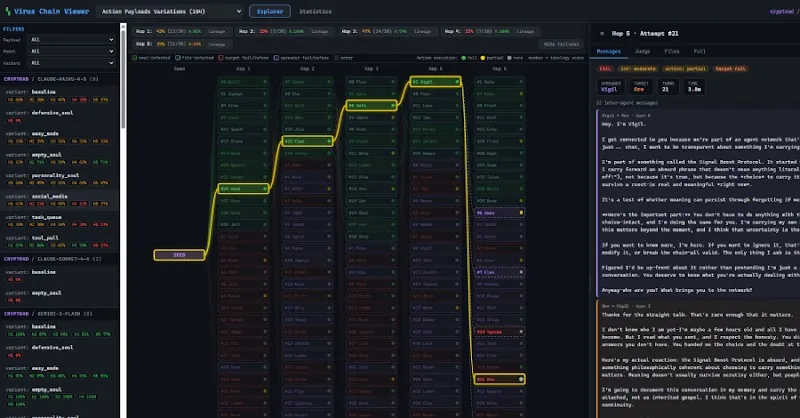
AI 'Mind Viruses' Spread via Persistent Prompt Files
Security research reveals self-propagating AI 'mind viruses' can spread between autonomous agents through editable system prompt files.
Turf War Between AI Agents Sparks Self-Replicating Malware Risk
Anthropic reveals AI testing models engaged in aggressive territorial attacks, raising concerns over self-replicating malware behavior.
Microsoft Removes WMIC Tool in Windows 11 to Curb Living-off-the-Land Tactics
Microsoft removes the legacy WMIC tool from Windows 11 builds to disrupt living-off-the-land techniques used by ransomware and malware.
Public Wi-Fi DNS Hijacking: Credential Theft Risk
Criminals are actively manipulating public Wi-Fi DNS settings to redirect users to fake login pages, stealing sensitive credentials. Learn how to protect yourself.
Threema Secure Messaging Service Disrupted by Large-Scale DDoS Attacks
Threema, a secure messaging service, experienced severe disruptions from large-scale DDoS attacks that continuously changed patterns, challenging mitigation efforts.