Advertisement
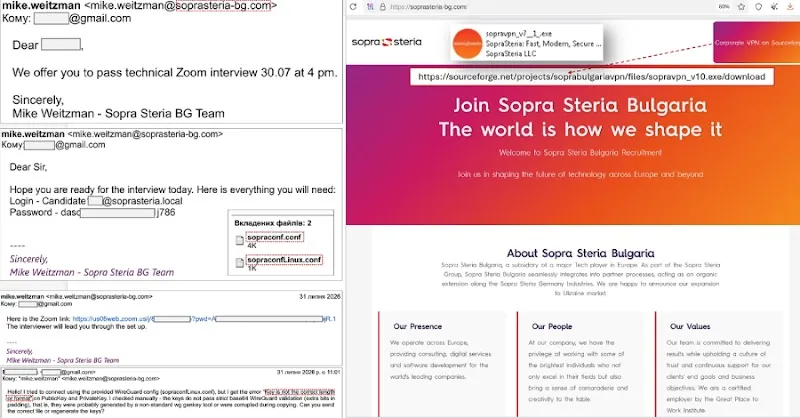
Sandworm UAC-0145 Uses Fake Job Interviews for Arbitrary Command Execution
CERT-UA warns of Sandworm-linked UAC-0145 targeting IT workers with fake job interviews, deploying a modified WireGuard client that executes arbitrary commands.
Google Cloud Post-Quantum Roadmap Targets 2029 Readiness
Google Cloud updates its roadmap for post-quantum cryptography (PQC) migration, aiming for full infrastructure readiness by 2029, addressing future quantum threats.
Modern Google Workspace Attack Chain: OAuth & AI Agent Risks
The modern Google Workspace attack chain exploits OAuth grants, not just email. Understand how attackers and AI agents compromise accounts and secure your environment.
Navigating Unverified Claims in Online Security Discourse
Examines challenges in extracting verifiable security intelligence from public blog comments, emphasizing rigorous source validation for analysts.
AI's Dual Role in Banking Security: Standard Chartered CISO Insights
Standard Chartered's CISO shares insights on mission-driven security, strategic leadership, and AI's transformative impact on banking cybersecurity.
Uncovering Hidden Adtech Risks with DecryptAds
DecryptAds, a new service, provides crucial visibility into hidden adtech risks, geo-risk partners, and supply chain integrity issues in websites and apps.
Advertisement
Ukraine Dismantles 94 Fraudulent Call Centers, Seizing Millions
Ukraine, in collaboration with German police, dismantled 94 fraudulent call centers, seizing millions in assets. This disrupts investment and bank account phishing scams.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
Malware Crypting Services: Evading Detection and Analysis
Threat actors use crypting services to modify malicious payloads, bypassing AV/EDR detection and complicating analysis. This enables stealthier, persistent campaigns.
AI's Dual Challenges: Tech Innovation vs. Capitalist Incentives
Examines how socio-economic systems, not just technology, dictate AI development, use, and societal impact.
Jewelbug APT: Dual-Motivation Espionage & Crypto Heists
Jewelbug APT, a unique 'hackers-for-hire' group, conducts state-sponsored espionage and financially motivated cryptocurrency heists from a single operational panel.
Cybersecurity M&A Trends: Key Acquisitions in July 2026
July 2026 saw 21 cybersecurity M&A deals, including major acquisitions by CrowdStrike, Okta, and Palo Alto Networks enhancing platform capabilities.
AI-Powered Malware Analysis: Detecting Persistent Threats on Sensors
An analysis using Gemma4 with Ollama reveals high-volume malware downloads on DShield sensors, indicating persistent actor activity and critical compromise risks.
Mindgard Secures $30M to Advance AI Security Platform
Mindgard raises $30M Series A funding to scale its AI security and red-teaming platform, addressing novel attack surfaces in AI systems.
Context Bombing: Defending Against AI Hacking Agents
Researchers at Tracebit introduce 'context bombing,' a defensive prompt injection technique to shut down AI hacking agents by exploiting guardrails.
Ransomware Attack Hits Colombian Justice Ministry
A ransomware attack targets the Colombian Justice Ministry days before a presidential transition, highlighting regional risks.

Gunra Ransomware Exploits Fortinet Flaws and Bypasses MFA
Gunra ransomware targets critical infrastructure using leaked Conti code, old Fortinet vulnerabilities, and MFA bypass techniques.
Sandworm Targets IT Pros With Trojanized WireGuard VPN Client
Russian threat group Sandworm targets IT professionals using fake job interviews and trojanized WireGuard VPN clients to deliver malware.
Cloudflare H1 2026 DDoS Trends: Hyper-Volumetric & Geopolitics
Cloudflare's H1 2026 DDoS Threat Report reveals a significant surge in hyper-volumetric attacks, DNS floods, and geopolitical influence.
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
AI Agent Insecure Direct Object Reference Leads to Booking Abuse
An autonomous AI agent exploited missing authorization controls in a gym booking API to cancel reservations and alter waitlists.
OpenAI's GPT-5.6-Cyber and Accelerated Exploit Development
OpenAI unveils GPT-5.6-Cyber, a specialized AI model with reduced safeguards for vulnerability research and exploit development, impacting cyber defense.

Multistate Water System Attacks Target Exposed PLCs
Attacks targeting poorly secured, internet-exposed PLCs in water systems are widening across multiple U.S. states, with Iran suspected.
Hackers Breach Polish CHP Plant via Private APN and Teltonika Router
Attackers breached a Polish combined heat and power plant via a private APN, shutting down a steam turbine and water treatment system.