Advertisement
CVE-2026-20127: Cisco Catalyst SD-WAN Exploited — Patch Guide
WatchTowr reports widespread exploitation attempts targeting a recent CVE-2026-20127 vulnerability in Cisco Catalyst SD-WAN devices, urging immediate action.

Firefox 148 Security Update: Anthropic AI Uncovers 22 Vulnerabilities
Anthropic's Claude Opus 4.6 AI model identified 22 security vulnerabilities in Firefox, including 14 high-severity flaws addressed in the version 148 release.

OpenAI Codex Security: Scanning 1.2 Million Commits for Vulnerabilities
OpenAI's Codex Security identifies over 10,000 high-severity vulnerabilities across 1.2 million commits using AI-driven detection and automated remediation.
Apple iOS CVE-2023-41993: Patching Exploited Spyware Vulnerabilities
CISA warns of three Apple iOS vulnerabilities, including CVE-2023-41993, exploited in mercenary spyware and cryptocurrency theft attacks. Patch immediately.

Hikvision and Rockwell Automation CVEs: CISA KEV Mitigation Guide
CISA adds Hikvision CVE-2017-7921 and Rockwell Automation flaws to the KEV catalog. Learn how to detect and mitigate these critical CVSS 9.8 vulnerabilities.
CVE-2024-28182: Python Cryptography RSA DoS Mitigation Guide
Technical deep dive into CVE-2024-28182, a denial-of-service vulnerability in the Python cryptography library. Learn how to detect and patch RSA-based DoS.
Advertisement
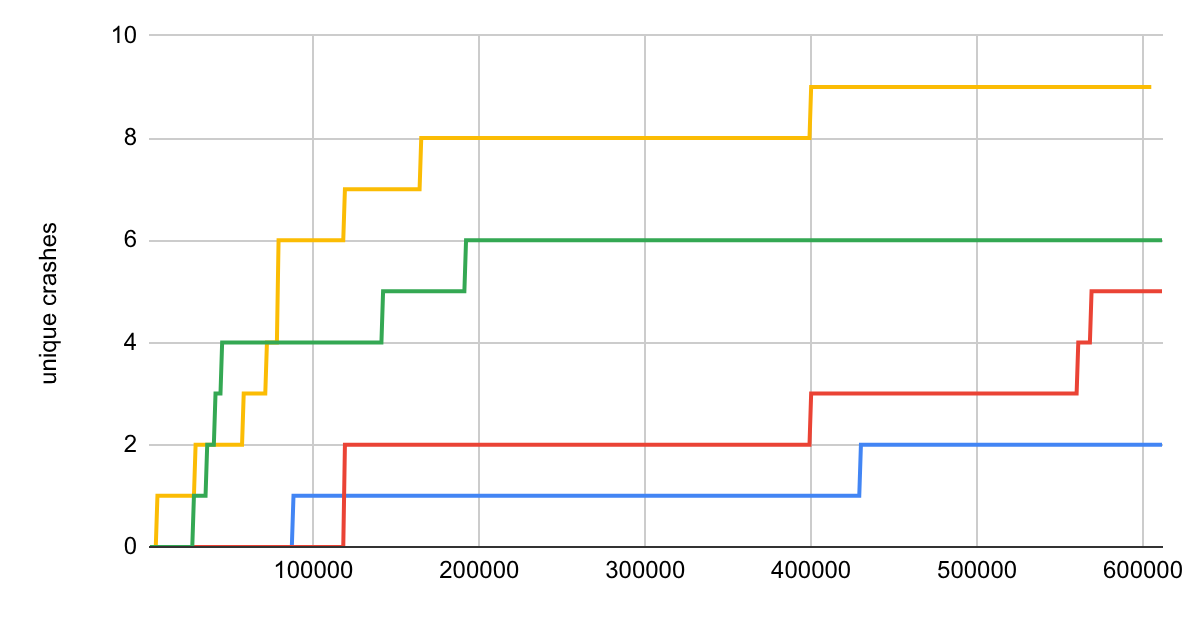
Optimizing Mutational Grammar Fuzzing for Enhanced Vulnerability Discovery
Explore the effectiveness and inherent flaws of mutational grammar fuzzing, a key technique for vulnerability discovery, and a method to improve its efficacy.
CISA KEV Update: Five Actively Exploited CVEs in Apple, Hikvision, Rockwell
CISA adds five actively exploited vulnerabilities, including Apple iOS/iPadOS use-after-free and Hikvision improper authentication, to its KEV Catalog.
CVE-2026-3094: Delta CNCSoft-G2 Out-of-bounds Write RCE
Delta Electronics CNCSoft-G2 is vulnerable to an out-of-bounds write (CVE-2026-3094) allowing remote code execution. Update to V2.1.0.39.
WordPress User Registration & Membership Plugin: Admin Account Exploit
Critical vulnerability in WordPress User Registration & Membership plugin actively exploited to create unauthorized admin accounts.

CVE-2026-20122: Cisco Catalyst SD-WAN Manager Exploited in the Wild
Cisco confirms active exploitation of CVE-2026-20122 in Catalyst SD-WAN Manager, allowing authenticated attackers to perform arbitrary file overwrites.
Microsoft Outlook CVE-2025-21418: Mitigating NTLM Relay Attacks
Analysis of CVE-2025-21418 in Microsoft Outlook. Learn how attackers bypass security features to leak NTLM hashes and the steps needed for mitigation.
Reclaim Security Secures $20M to Automate Vulnerability Remediation
Reclaim Security raises $20 million to solve the remediation gap, focusing on automating fixes and reducing mean time to remediate for enterprise SOC teams.
Cisco Catalyst SD-WAN Manager Exploitation: Patch CVE-2024-20437 Now
Cisco confirms active exploitation of two high-severity flaws in Catalyst SD-WAN Manager, involving hardcoded credentials and authentication bypass.
Cisco Catalyst SD-WAN Manager CVE-2023-20252 — Mitigation Guide
Cisco warns of active exploitation targeting Catalyst SD-WAN Manager vulnerabilities CVE-2023-20252 and CVE-2023-20253. Immediate patching is required.
Mail2Shell Zero-Click RCE Threatens FreeScout Servers
A critical Mail2Shell zero-click vulnerability in FreeScout helpdesk allows unauthenticated remote code execution, granting full server control.
Cisco Secure FMC Root Access & DoS Flaws Patched: Update Now
Cisco addresses two maximum-severity vulnerabilities in Secure Firewall Management Center (FMC) allowing unauthenticated root access and denial of service.
CVE-2025-22719: VMware Aria Operations RCE Exploited in the Wild
CVE-2025-22719 is a critical remote code execution vulnerability in VMware Aria Operations for Networks currently being exploited by unauthenticated attackers.

VMware Aria Operations CVE-2026-22719 Exploited - Mitigation Guide
CISA adds CVE-2026-22719, a VMware Aria Operations command injection flaw, to the KEV catalog following active exploitation. Secure your systems now.
CVE-2025-0282: Ivanti Connect Secure Heap Overflow — Mitigation Guide
Technical analysis of the Ivanti Connect Secure heap overflow (CVE-2025-0282) allowing unauthenticated RCE. Includes detection steps and patch guidance.
Hitachi Energy RTU500 CMU Firmware Vulnerabilities: Patch Guidance
Hitachi Energy issues critical patches for RTU500 series CMU firmware addressing high-severity DoS and information disclosure risks (CVE-2026-1773, CVE-2024-8176).
CVE-2023-20887: VMware Aria Operations for Networks RCE Exploit Guide
CISA adds CVE-2023-20887 to its KEV catalog. Learn how to detect and patch this critical RCE flaw in VMware Aria Operations for Networks.
Mobiliti e-mobi.hu EV Chargers: Critical Auth Bypass & DoS Vulnerabilities
Critical vulnerabilities in Mobiliti e-mobi.hu EV charging stations (all versions) allow unauthenticated attackers to gain administrative control or disrupt services.
Google Chrome Two-Week Release Cycle: Reducing the Patch Gap
Google transitions Chrome to a two-week stable release cycle to accelerate security patching and minimize the window for n-day vulnerability exploitation.