Advertisement
Microsoft March Update: 83 CVEs Patched, Prioritization Key
Microsoft's March Patch Tuesday addresses 83 CVEs across its product line. Learn why applying these security updates is crucial for defending against potential…
March 2026 Patch Tuesday: Microsoft Fixes 77 Vulnerabilities
Microsoft's March 2026 Patch Tuesday addresses 77 vulnerabilities across Windows and other software. Learn about the risks and how to prioritize patching.
Microsoft Patch Tuesday March 2026: 8 Critical Vulnerabilities Addressed
Microsoft's March 2026 Patch Tuesday addresses 93 vulnerabilities, including 8 critical issues across various products and 9 in Microsoft Edge (Chromium).
CVE-2025-57176: Unauthenticated File Upload in Ceragon Siklu Devices
An unauthenticated file upload vulnerability (CVE-2025-57176) in Ceragon Siklu MultiHaul and EtherHaul series devices poses risks to critical communications…
CVE-2026-3611: Critical Auth Bypass in Honeywell IQ4x BMS Controllers
CISA warns of a critical authentication bypass (CVE-2026-3611) in Honeywell IQ4x BMS Controllers, allowing unauthenticated attackers administrative access and potential…
Adobe Security Update: 80 Vulnerabilities Across 8 Products Patched
Adobe's comprehensive security update addresses 80 vulnerabilities across 8 products, including Commerce, Acrobat Reader, and Premiere Pro. Immediate patching is vital.
Advertisement
Microsoft Patch Tuesday: 83 Vulnerabilities, Critical Flaw Addressed
Microsoft's latest Patch Tuesday addresses 83 vulnerabilities across its product line, including one critical flaw. Security teams must prioritize immediate patching.
Windows 10 KB5078885 ESU Fixes Two Zero-Days — Patch Guidance
Microsoft releases Windows 10 KB5078885 Extended Security Update to address two zero-day vulnerabilities and a critical system shutdown bug for ESU subscribers.

FortiGate NGFW Exploitation Leads to Service Account Credential Theft
Threat actors are exploiting FortiGate devices to extract configuration files and steal service account credentials, facilitating lateral movement in networks.
Ivanti EPM CVE-2024-29824 Exploited: Technical Analysis and Patching
CISA warns of active exploitation of CVE-2024-29824 in Ivanti Endpoint Manager. Secure your Core server with our technical analysis and mitigation guide.
Microsoft Windows Hotpatching to be Enabled by Default in May 2026
Microsoft will enable hotpatching by default for Intune-managed Windows devices in May 2026, allowing security updates without reboots to reduce downtime.
CVE-2024-29847: Ivanti EPM RCE Under Active Exploitation - Patch Now
CISA warns of active exploitation of a critical Ivanti EPM vulnerability (CVE-2024-29847). Learn how to mitigate this unauthenticated RCE threat immediately.

CISA Flags SolarWinds, Ivanti, and Workspace One Flaws in KEV Update
CISA adds vulnerabilities in SolarWinds, Ivanti, and Omnissa Workspace One UEM to its Known Exploited Vulnerabilities catalog following active exploitation.
CVE-2026-1603: CISA Warns of Active Ivanti and SolarWinds Exploitation
CISA adds CVE-2026-1603, CVE-2025-26399, and CVE-2021-22054 to the KEV catalog, requiring immediate remediation for Ivanti, SolarWinds, and Omnissa systems.
AirSnitch: Cross-Layer Desynchronization Enables Wi-Fi MitM Attacks
Research reveals AirSnitch, a vulnerability exploiting Wi-Fi Layers 1 and 2 to execute bidirectional MitM attacks across home and enterprise networks.
CVE-2026-20127: Cisco Catalyst SD-WAN Exploited — Patch Guide
WatchTowr reports widespread exploitation attempts targeting a recent CVE-2026-20127 vulnerability in Cisco Catalyst SD-WAN devices, urging immediate action.

Firefox 148 Security Update: Anthropic AI Uncovers 22 Vulnerabilities
Anthropic's Claude Opus 4.6 AI model identified 22 security vulnerabilities in Firefox, including 14 high-severity flaws addressed in the version 148 release.

OpenAI Codex Security: Scanning 1.2 Million Commits for Vulnerabilities
OpenAI's Codex Security identifies over 10,000 high-severity vulnerabilities across 1.2 million commits using AI-driven detection and automated remediation.
Apple iOS CVE-2023-41993: Patching Exploited Spyware Vulnerabilities
CISA warns of three Apple iOS vulnerabilities, including CVE-2023-41993, exploited in mercenary spyware and cryptocurrency theft attacks. Patch immediately.

Hikvision and Rockwell Automation CVEs: CISA KEV Mitigation Guide
CISA adds Hikvision CVE-2017-7921 and Rockwell Automation flaws to the KEV catalog. Learn how to detect and mitigate these critical CVSS 9.8 vulnerabilities.
CVE-2024-28182: Python Cryptography RSA DoS Mitigation Guide
Technical deep dive into CVE-2024-28182, a denial-of-service vulnerability in the Python cryptography library. Learn how to detect and patch RSA-based DoS.
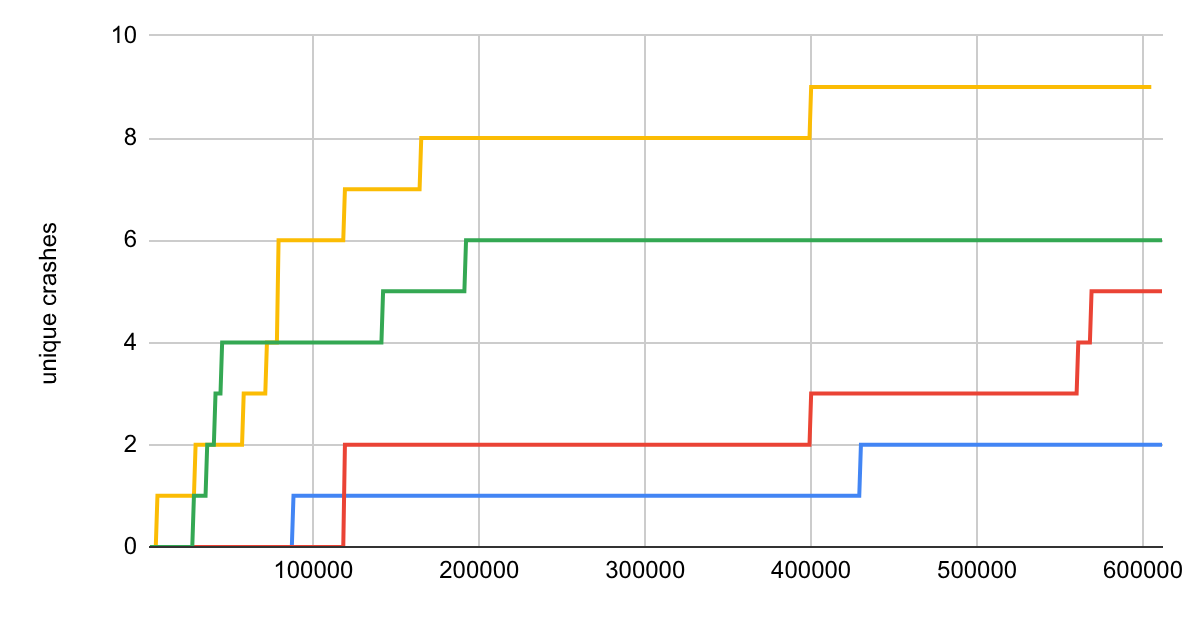
Optimizing Mutational Grammar Fuzzing for Enhanced Vulnerability Discovery
Explore the effectiveness and inherent flaws of mutational grammar fuzzing, a key technique for vulnerability discovery, and a method to improve its efficacy.
CISA KEV Update: Five Actively Exploited CVEs in Apple, Hikvision, Rockwell
CISA adds five actively exploited vulnerabilities, including Apple iOS/iPadOS use-after-free and Hikvision improper authentication, to its KEV Catalog.
CVE-2026-3094: Delta CNCSoft-G2 Out-of-bounds Write RCE
Delta Electronics CNCSoft-G2 is vulnerable to an out-of-bounds write (CVE-2026-3094) allowing remote code execution. Update to V2.1.0.39.