Advertisement
Ransomware Payment Rates Hit All-Time Low Despite Surge in Attacks
Ransomware payment rates dropped to a record 28% in 2023 as organizations improve recovery and face increasing legal pressure against paying threat actors.

Threat Intelligence Analysis: Kali Linux AI Integration and Browser Crash Traps
Analysis of Kali Linux Claude AI integration, Chrome browser crash traps, and the ongoing exploitation of WinRAR vulnerabilities by LockBit affiliates.

UAT-10027 Deploys Dohdoor Backdoor via DNS-over-HTTPS
UAT-10027 targets U.S. healthcare and education sectors using the novel Dohdoor backdoor, leveraging DNS-over-HTTPS for stealthy C2 communication.
US Sanctions Russian Exploit Broker Operation Zero
US Treasury sanctions Russian exploit broker Operation Zero and its owner Sergey Zaytsev for facilitating zero-day trades with Russian intelligence agencies.

Microsoft Warns of Fake Next.js Repos Delivering In-Memory Malware
Microsoft warns developers of a coordinated campaign using malicious Next.js repositories disguised as job assessments to deliver in-memory malware.
Hypervisor-Based Persistence: Abusing Virtual Machines for Stealth
Analysis of how threat actors leverage virtualization platforms to host malicious guest OSs, bypassing host-level EDR and maintaining persistent access.
Advertisement
Optimizing Honeypot Log Analysis Using AI and LLM Orchestration
An analysis of how AI-assisted log processing reduces noise in DShield and Cowrie honeypot data, enabling analysts to identify sophisticated threat patterns.
CLAIR Model: Mapping Critical Infrastructure Interdependencies
The CLAIR Model is a conceptual framework designed to map complex interdependencies within critical infrastructure, enhancing resilience and risk assessment.
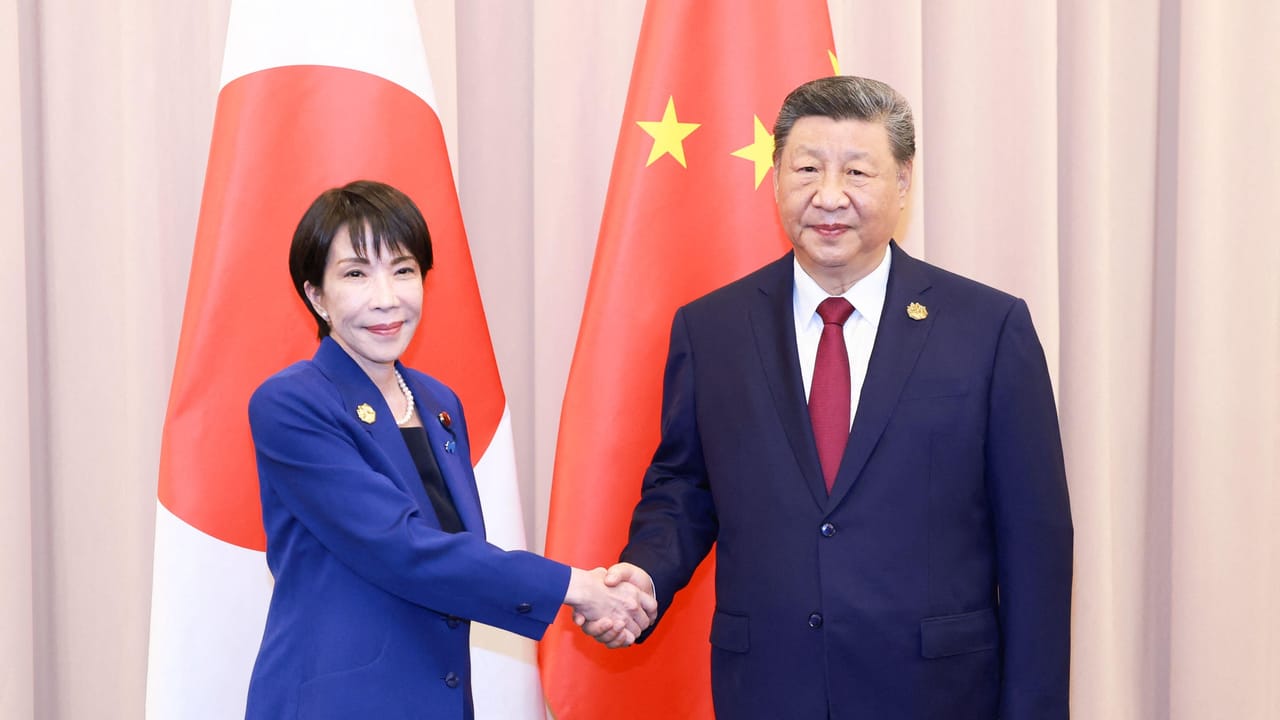
Chinese Police Use ChatGPT in Influence Operations Against Japan
Chinese police reportedly used ChatGPT for politically motivated influence operations to smear Japan's PM Takaichi, highlighting AI's role in disinformation campaigns.
Cisco SD-WAN Exploitation: Critical Authentication Bypass & Escalation
CISA alerts on active global exploitation of Cisco SD-WAN, leveraging CVE-2026-20127 for initial access and CVE-2022-20775 for privilege escalation.
Chinese Cyberspies Exploit SaaS APIs in Global Espionage Campaign
A suspected Chinese threat actor breached dozens of telecom firms and government agencies, using SaaS API calls to evade detection in a global espionage campaign.

Google Disrupts UNC2814 GRIDTIDE Infrastructure After 53 Breaches
Google disrupts infrastructure of China-nexus threat actor UNC2814 (GRIDTIDE) after 53 breaches across 42 countries targeting government and telecom sectors.
GRIDTIDE Espionage: PRC-Nexus UNC2814 Targets Telecoms Globally
Google disrupts GRIDTIDE, a novel backdoor used by PRC-nexus UNC2814 for global cyber espionage against telecommunications and government entities.
TOAD Emails: The 'Call This Number' Gateway Bypass Threat
Attackers use Telephone-Oriented Attack Delivery (TOAD) with 'call this number' emails to bypass gateways, relying on social engineering post-call.
Google Disrupts Chinese Espionage Actor UNC2814 Targeting Telecoms
Google and Mandiant disrupt UNC2814, a Chinese state-sponsored actor active since 2017, targeting 42 countries across telecom and government sectors.
Stolen Credentials and the Escalation of Agentic AI Attacks
IBM X-Force reports 56% of 2025 vulnerabilities require no authentication, enabling agentic AI to weaponize stolen credentials and expand attack blast radius.
OpenClaw Underground Trends: Assessing Hype vs. Operational Risk
Flare telemetry reveals a gap between high OpenClaw chatter on Telegram and actual exploitation, highlighting the need to distinguish hype from threat.

Optimizing Incident Triage to Mitigate Enterprise Business Risk
Examine how inefficient security incident triage increases business risk, escalates operational costs, and leads to missed SLAs in the modern SOC.

SLH Recruits Women for $1,000 IT Help Desk Vishing Attacks
Scattered LAPSUS$ Hunters (SLH) are offering financial incentives to recruit women for vishing campaigns targeting corporate IT help desks and IAM systems.
Data Poisoning Risks in Real-Time AI Search and Ingestion
A recent experiment highlights how rapid web scraping for AI models like Gemini and ChatGPT enables data poisoning attacks through unverified web content.

Quantitative Scoring for OT Incidents: The Richter Scale Model
Analysis of a new logarithmic scoring system designed to quantify the physical magnitude and technical severity of operational technology (OT) cyberattacks.
Cybersecurity M&A Trends 2025: Analysis of 426 Industry Deals
SecurityWeek reports 426 cybersecurity M&A deals in 2025, highlighting a disciplined market shift toward GRC, data protection, and identity management.
Ex-L3Harris Executive Sentenced for Selling Zero-Days to Russia
Former Trenchant CEO James Michael Robinson sentenced to 90 months for stealing zero-day exploits and selling them to a Russian state-linked broker.
US Treasury Sanctions Russian Broker for Stolen Zero-Day Exploits
The US sanctions Artem Kruglov and associated firms for brokering stolen hacking tools and zero-day exploits for Russian intelligence services.