Advertisement

L3Harris Insider Sentenced for Selling Zero-Days to Russian Broker
Former defense contractor Peter Williams sentenced to seven years for selling eight zero-day exploits to Russian broker Operation Zero for millions in profit.

National Security Risks of Manual Data Transfer Processes
Report reveals 50% of national security organizations rely on manual data transfers, creating systemic risks and critical intelligence latency.
Interpol’s Operation Red Card 2.0: 651 Arrests Targeting Cybercrime
INTERPOL and AFRIPOL's Operation Red Card 2.0 disrupts West African cybercrime syndicates, leading to 651 arrests and $4.3 million in seized funds.
Windows 11 KB5077241: Native Sysmon Integration and BitLocker Updates
Microsoft integrates native Sysmon and enhances BitLocker management in the Windows 11 KB5077241 optional update, providing advanced telemetry for defenders.
Russia's Escalating New Generation Hybrid Warfare in Europe
Analysis of Russia's coordinated New Generation Warfare against NATO, blending cyber attacks, sabotage, and influence operations. Understand the threat.
AI-Enabled Threats: Model Extraction, APT Phishing, & Malware Evolution
GTIG reports on Q4 2025 AI threats: rising model extraction, APTs using AI for reconnaissance and phishing, and new AI-integrated malware families like HONESTCUE and…
Advertisement
UNC6201 Exploits Dell RecoverPoint Zero-Day CVE-2026-22769
Mandiant and GTIG detail UNC6201's exploitation of CVE-2026-22769 in Dell RecoverPoint for VMs, deploying GRIMBOLT backdoor and novel VMware TTPs.
Lazarus Group Shifts to Medusa Ransomware & Multi-Tool Attacks
North Korea's Lazarus Group now employs Medusa ransomware, Comebacker backdoor, Blindingcan RAT, and Infohook info stealer in recent attacks, signaling an evolving…
Attackers Halve Breakout Time to 29 Minutes, CrowdStrike Reports
CrowdStrike research indicates attackers now achieve lateral movement in just 29 minutes, driven by credential misuse, AI, and blind spots.
Diesel Vortex Phishing Campaign Targets Logistics Sector
Financially motivated Diesel Vortex group targets US & European freight and logistics with extensive phishing campaign, using 52 domains to steal credentials.

UAC-0050 Targets European Financial Institutions with RMS Malware
Russia-aligned actor UAC-0050 expands operations beyond Ukraine, targeting European financial entities with spoofed domains and RMS malware for espionage.
AI Influence Operations and the Erosion of Democratic Feedback
Bruce Schneier analyzes how AI-generated content overwhelms democratic institutions and creates an influence arms race, threatening institutional integrity.
Spanish Authorities Dismantle Anonymous Fénix Hacktivist Node
Spain's National Police arrested four members of Anonymous Fénix, a hacktivist group targeting government infrastructure with DDoS and data exfiltration.
Lazarus Group Targets U.S. Healthcare with Medusa Ransomware
North Korean Lazarus Group is targeting U.S. healthcare providers with Medusa ransomware, utilizing Dtrack malware for initial access and persistence.

UnsolicitedBooker Targets Central Asian Telecoms via LuciDoor Backdoor
The UnsolicitedBooker threat actor has pivoted to targeting telecommunications providers in Kyrgyzstan and Tajikistan using LuciDoor and MarsSnake backdoors.

Lazarus Group Deploys Medusa Ransomware in Global Healthcare Attacks
Lazarus Group (Diamond Sleet) targets Middle Eastern entities and U.S. healthcare with Medusa ransomware, according to Symantec and Carbon Black reports.
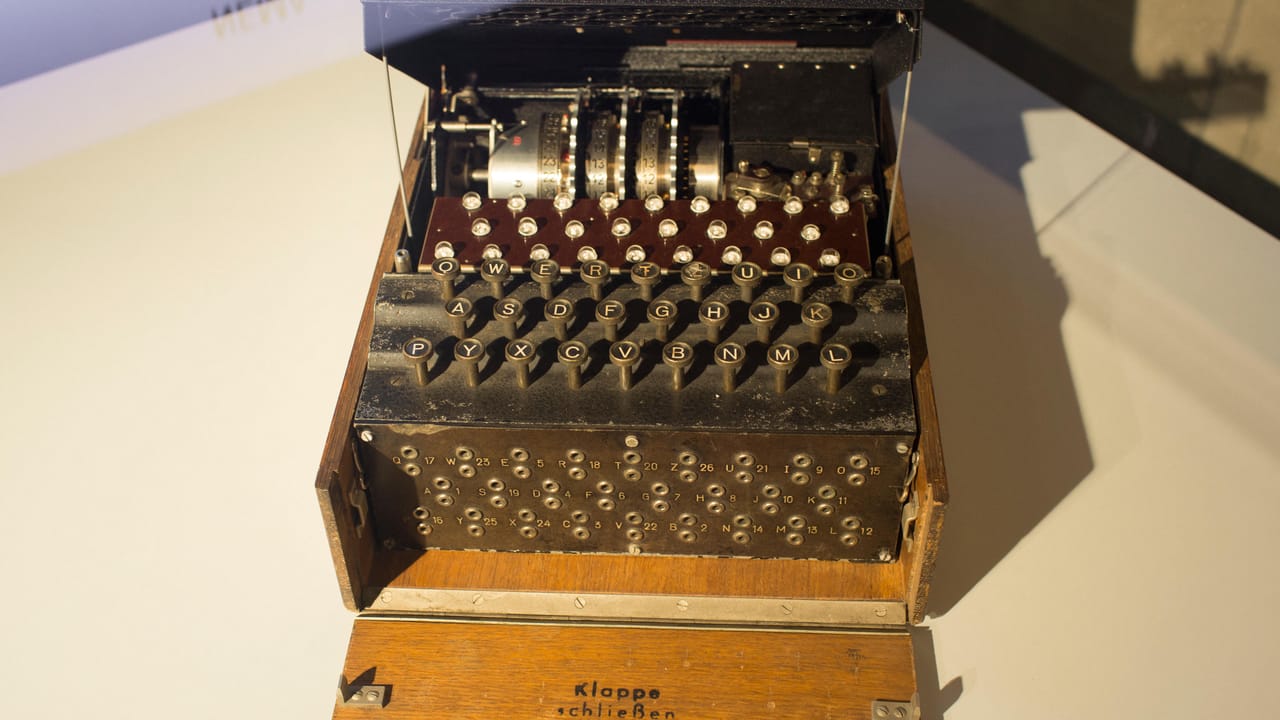
Operational Resilience: Cryptographic Lessons from the Enigma Device
An analysis of historical cryptographic failures within the Enigma machine and how these resilience errors inform modern cybersecurity defense strategies.

MuddyWater Deploys BugSleep Backdoor in Targeted Regional Campaigns
Iranian state actor MuddyWater introduces the custom BugSleep backdoor, targeting Middle Eastern and African entities using spear-phishing and RMM abuse.
ATM Jackpotting Trends: $20M Losses Driven by Legacy Exploits
ATM jackpotting surged in 2025, resulting in over $20 million in losses as threat actors leverage decade-old tools and black-box tactics against aging hardware.
Spanish Police Disrupt Anonymous Sudan Hacktivist DDoS Operations
Spanish authorities arrest three individuals linked to the Anonymous Sudan hacktivist group for executing DDoS attacks against government and critical infrastructure.

Anthropic Reports Industrial-Scale Model Distillation by Chinese Firms
Anthropic identifies DeepSeek, Moonshot AI, and MiniMax in a massive effort to copy Claude's capabilities via 16 million queries and 24,000 fake accounts.

APT28 Operation MacroMaze: Webhook-Driven Macro Execution Targeting Western Europe
Analysis of a targeted campaign attributed to APT28, utilizing macro-enabled documents and legitimate webhook services for command-and-control obfuscation.

Technical Analysis: Multi-Vector Threats Spanning Web Skimming, AI Prompt Injection, and Volumetric DDoS
A deep dive into redundant Magecart exfiltration techniques, PromptSpy AI exploitation frameworks, and the escalation of 30Tbps volumetric DDoS attacks.
Automated AI-Driven Exploitation of FortiGate Management Interfaces in AWS Environments
Threat actors are utilizing artificial intelligence to automate credential stuffing and exploit exposed administrative ports on Fortinet devices within AWS…