Advertisement
CyberStrikeAI Exploitation: AI Tools Targeting Fortinet Firewalls
Threat actors are repurposing CyberStrikeAI to automate reconnaissance and exploit critical vulnerabilities in Fortinet FortiGate firewalls and edge devices.
Sentencing in $24 Million Microsoft Licensing Fraud Scheme
A Florida woman has been sentenced to 22 months in prison for a multi-million dollar scheme involving stolen Microsoft Certificate of Authenticity labels.
Alabama Man Pleads Guilty to Extortion via Social Media Hijacking
Devin Deandre Moore admits to hijacking hundreds of accounts for sextortion. Analysis of the TTPs used in this large-scale digital extortion campaign.
Iranian Cyberattack Risks Escalate Amid Middle-East Conflict
The NCSC warns UK organizations of increased Iranian state-sponsored cyber threats targeting critical infrastructure and utilizing advanced phishing tactics.

SD-WAN Zero-Day and Smart TV Proxy SDK Vulnerabilities Recap
Technical analysis of recent SD-WAN zero-day exploits and Smart TV proxy SDK risks, detailing how network infrastructure is increasingly targeted.
LLM-Assisted Deanonymization: Scaling Automated Identity Discovery
New research highlights how LLM agents automate the deanonymization of anonymous online posts across Reddit and Hacker News with high precision and scale.
Advertisement
North Korean APT Bridges Air Gaps with New Malware Suite
North Korean threat actors utilize malicious LNK files and specialized USB propagation tools to compromise air-gapped networks. Analysis and defense guide.

APT28 Exploits CVE-2026-21513: MSHTML 0-Day Intelligence
Akamai reports Russia-linked APT28 exploited CVE-2026-21513 in the MSHTML Framework as a zero-day before Microsoft's February 2026 security patch updates.
Claude Code Weaponized in Mexican Government Cyberattack
Analysis of how threat actors leveraged Anthropic’s Claude Code to automate exploitation and exfiltrate 150GB of data from Mexico's infrastructure ministry.
Analysis of the Kimwolf Botnet and Threat Actor 'Dort'
An analysis of the Kimwolf botnet operator 'Dort', including retaliatory TTPs like DDoS, swatting, and the exploitation of undisclosed vulnerabilities.
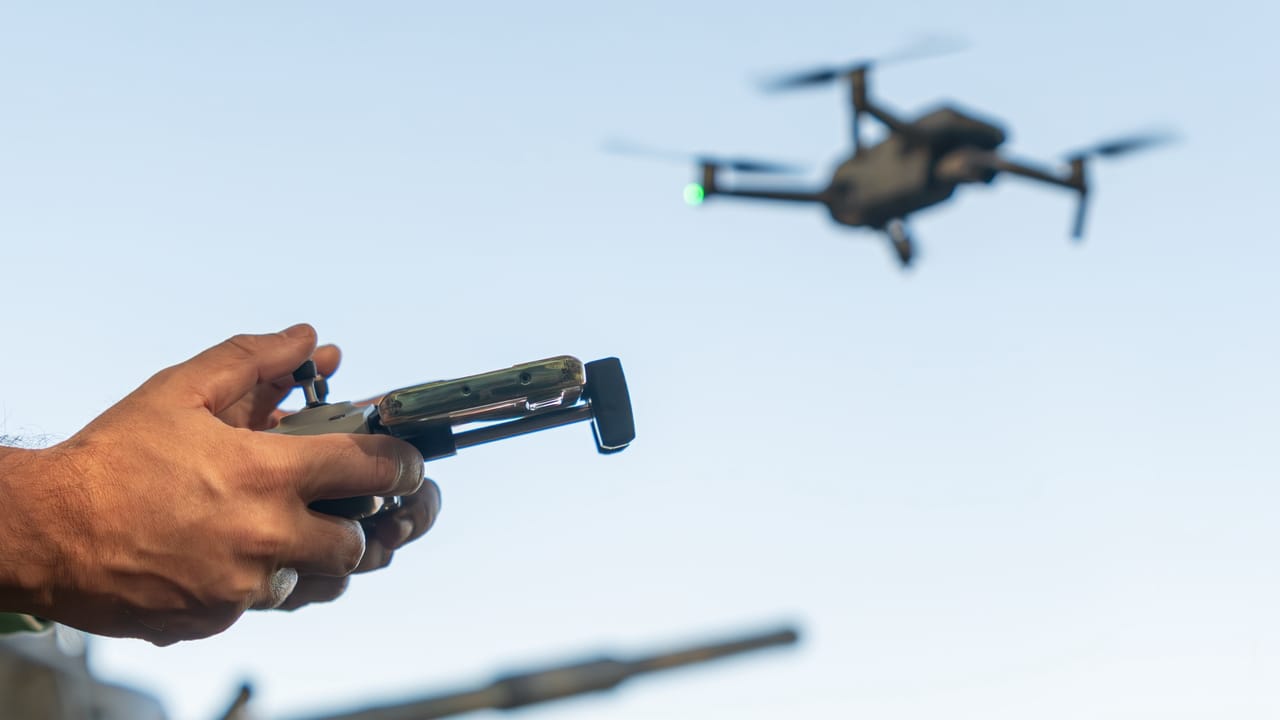
Enhancing Wireless & Drone Defense for Major Urban Events
As cities host major events, security posture must extend beyond traditional physical and cyber defenses to address complex wireless and drone threats.
Ransomware Realities: Singing River Health and Healthcare Resilience
Analysis of the ransomware attack on Singing River Health System, focusing on the Rhysida threat group and the technical impact of EHR downtime on patient care.
Federal Directive Mandates Phase-Out of Anthropic AI from U.S. Agencies
All U.S. federal agencies must discontinue Anthropic technology, impacting AI supply chains while OpenAI, Google, and xAI maintain their government contracts.
APT37 Deploys SHROUDEDVUE Malware to Target Air-Gapped Networks
North Korean threat actor APT37 utilizes new malware families like SHROUDEDVUE and WASHSYNC to infiltrate air-gapped systems via removable USB drives.
Windows 11 Hardens Batch File Execution to Counter Script Attacks
Microsoft tests security enhancements for batch and CMD files in Windows 11 Insider Build 27723 to mitigate Living-off-the-Land (LotL) script abuse.

DOJ Seizes $61M in Tether Linked to Global Pig Butchering Scams
The U.S. Department of Justice seized $61 million in Tether (USDT) tied to pig butchering investment fraud, marking a major blow to criminal laundering networks.
Claude Code Security Analysis: Assessing AI CLI Assistant Risks
Technical analysis of Anthropic's Claude Code CLI tool, evaluating its impact on application security and potential for introducing code vulnerabilities.
MITRE ATT&CK Governance and Predator Spyware iOS Evasion Tactics
Analysis of the new MITRE ATT&CK Advisory Council, Predator spyware bypassing iOS indicators, and Russian cyber-kinetic operation coordination.

ScarCruft Ruby Jumper Campaign Targets Air-Gapped Networks
North Korean threat actor ScarCruft (APT37) deploys Ruby Jumper campaign using Zoho WorkDrive for C2 and USB malware to target air-gapped environments.
Fake Recruiters Deploy Malware via Malicious Coding Challenges
North Korean threat actors are targeting software developers with fake job offers and malicious coding tests to deploy malware on developer workstations.
Analysis of Iran's 2026 Total Internet Shutdown and NIN Architecture
Technical review of Iran's National Information Network and the shift toward total communications blackouts as a tool for state-level control.

Meta Files Lawsuits Against Global Celeb-Bait Scam Networks
Meta takes legal action against advertisers in Brazil, China, and Vietnam, disabling accounts and domains used in large-scale celebrity-bait fraud schemes.
Strategic Board Oversight: Supply Chain, AI, and Regulatory Risks
An analysis of critical cybersecurity risks for board oversight, covering supply chain integrity, AI weaponization, and regulatory liability requirements.
Recorded Future Integrates CYBERA Data to Combat Money Mule Networks
Recorded Future partners with CYBERA to integrate verified scam-linked bank account data, enhancing payment fraud detection and money mule mitigation efforts.