Advertisement
Ransom Busters Ransomware Affiliate Poses as Recovery Firm
A ransomware affiliate masquerades as an incident recovery service to intercept victims, divert negotiations, and manipulate ransom payments.
Microsoft Removes WMIC Tool in Windows 11 to Curb Living-off-the-Land Tactics
Microsoft removes the legacy WMIC tool from Windows 11 builds to disrupt living-off-the-land techniques used by ransomware and malware.
Clop Ransomware Exploits CVE-2026-12569 in PTC Products
Shell investigates potential data theft by Clop gang after exploitation of critical CVE-2026-12569 in PTC Windchill and FlexPLM instances.
Data Analyst Sentenced to Prison for Extorting Brightly Software
A former data analyst contractor was sentenced to two years in prison for orchestrating a $2.5 million cryptocurrency extortion scheme against Brightly.
Picus Blue Report 2026: Enterprise Edge Defenses vs Post-Compromise
Analysis of the Picus Labs Blue Report 2026 reveals strong enterprise perimeter defenses, but severe blind spots for internal reconnaissance and credential theft.
Ransomware Attack Hits Colombian Justice Ministry
A ransomware attack targets the Colombian Justice Ministry days before a presidential transition, highlighting regional risks.
Advertisement
Gunra Ransomware Exploits Fortinet Flaws and Bypasses MFA
Gunra ransomware targets critical infrastructure using leaked Conti code, old Fortinet vulnerabilities, and MFA bypass techniques.
Deadlock Ransomware Uses Blockchain for C2 Resilience
Deadlock ransomware uses Polygon blockchain smart contracts and Session to resist infrastructure takedown and evade law enforcement.
Geopolitical AI Supply Chain Threats and Cyber Espionage
Examine how state-sponsored threat groups and criminal syndicates target the global AI supply chain, from rare earth minerals to silicon chips.
Hackers Breach Polish CHP Plant via Private APN and Teltonika Router
Attackers breached a Polish combined heat and power plant via a private APN, shutting down a steam turbine and water treatment system.
SonicWall SMA1000 Exploited: Ransomware Targets CVE-2026-15409/15410
CISA confirms ransomware exploitation of SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410, urging immediate patching.
AI-Driven Vulnerability Surges and UAT-11795 Starland RAT Campaign
Analysis of a record Patch Tuesday driven by AI vulnerability research, alongside Cisco Talos findings on UAT-11795 deploying Starland RAT.
Cisco Talos Previews AI Threats and Warlock Ransomware at Black Hat
Cisco Talos outlines research on AI threat actor tactics, Warlock ransomware, and agent identity security ahead of Black Hat USA 2026.
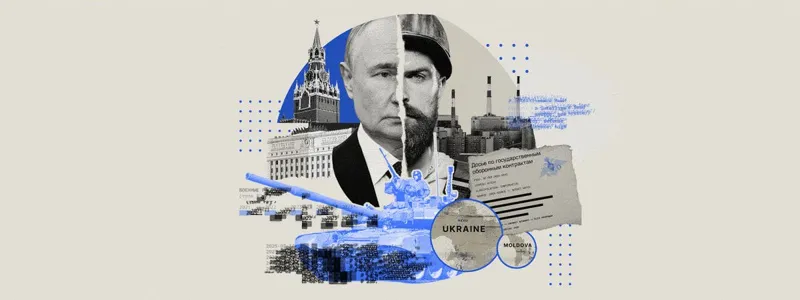
Russia's Defense Economy and Ongoing Cyber and Physical Threats
Analysis of Russia's defense-based economy, rising military spending, elite patronage networks, and the resulting high-risk threat environment.
Q2 2026 IR Trends: Phishing, MFA Bypass, RMM Tool Abuse
Talos Q2 2026 incident response data shows rising phishing and MFA bypass, with new actors like UAT-11764 and Sinobi ransomware leveraging RMM tools.
Emerging Cyber Threats and Espionage Risks in Neurotechnology
Examine growing security threats to neurotechnology and brain-computer interfaces, focusing on IP theft, biometric data collection, and state-sponsored espionage.
UNC6671 Rebrands: Multi-Brand Vishing and Cloud Extortion
Google Threat Intelligence Group tracks UNC6671 shifting through Redact, Pink, Helix, and Falcon extortion brands while targeting cloud environments.
Canadian Threat Actor Pleads Guilty in Snowflake Extortions
Connor Riley Moucka pleaded guilty to computer fraud and extortion involving 165 Snowflake client organizations and AT&T customer records.
Automated SSH Actors Achieve Persistence in 22 Seconds
Analysis of a Cowrie SSH honeypot reveals automated threat actors moving from credential compromise to system persistence in just 22 seconds.
Talos Q2 2026 Report: Phishing and Living-off-the-Land Trends
Cisco Talos Q2 2026 report reveals spikes in MFA-bypassing phishing and malicious use of remote management tools.
Ransom Cartel Ransomware Creator Sentenced to 16 Years in Prison
Maksim Silnikau, creator of the Ransom Cartel ransomware operation, receives a 16-year prison sentence following international law enforcement cooperation.
Smoke#Screen RMM Takeover Campaign Targets Enterprise Networks
Discover how the Smoke#Screen phishing campaign uses rotating payloads and ScreenConnect to achieve persistent remote network access.

Operation Cronos: FBI's Strategy to Disrupt LockBit Ransomware-as-a-Service
Analysis of Operation Cronos's success in disrupting LockBit, focusing on how law enforcement leveraged affiliate trust to dismantle the ransomware giant.
Coca-Cola Subsidiary Fairlife Impacted by Ransomware Data Theft
The Coca-Cola Company confirms a data breach at subsidiary Fairlife following a ransomware attack. Learn about the impact and mitigation strategies.