Advertisement
PTC Windchill RCE via CVE-2022-25247 — Mitigation Guide
Attackers are exploiting a critical deserialization flaw in PTC Windchill PLM software to deploy ransomware. Learn how to detect and patch CVE-2022-25247.
Ransomware as a Defensive Metric: Leveraging AI for Attack Path Remediation
Learn why ransomware reveals architectural defense gaps. This analysis explains how AI and proactive threat intelligence can fortify defenses and remediate critical…
Multi-Threat Brief: AI Malware, Zimbra Exploits, Linux Kernel Flaws
Analysis of recent threats including DolphinX AI malware, state-sponsored Zimbra exploits, Siemens industrial switch vulnerabilities, and 400 Linux kernel flaws.
PTC Windchill and FlexPLM Targeted in Clop Data Theft Campaign
Clop ransomware targets PTC Windchill and FlexPLM systems. Learn about the CVE-2022-25247 exploit risks and how to secure exposed PLM instances from extortion.
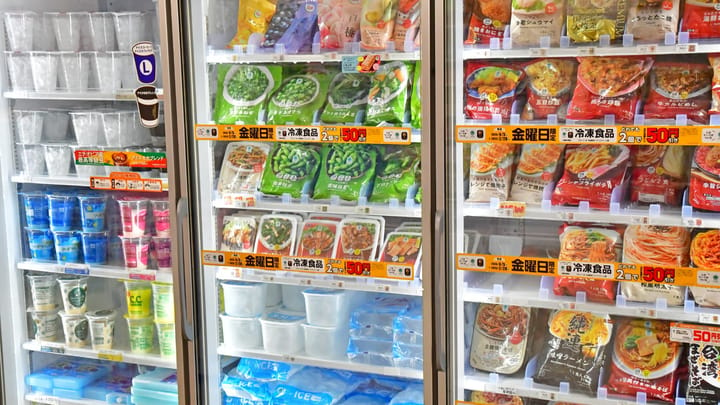
Ransomware Attack Freezes Japanese Food Supply Chain Operations
A ransomware attack on a Japanese food and logistics firm severely disrupted frozen food supply to thousands of clients, including KFC. Analyze the impact.
Enterprise GenAI Amplifies Ransomware Risk: Containment Strategies
Enterprise GenAI tools can accelerate ransomware attacks by inheriting excessive permissions.
Advertisement
Everest Ransomware Targets Stadler Rail's Supply Chain
Stadler Rail faced a $12.3M ransom demand from Everest ransomware after a data breach affecting a supplier data exchange platform.
PAN-OS GlobalProtect Authentication Bypass Exploited by Qilin
The Qilin ransomware gang is actively exploiting a critical Palo Alto Networks PAN-OS GlobalProtect authentication bypass vulnerability to breach corporate networks.

ENCFORGE Ransomware Targets AI Systems via Langflow RCE
New ENCFORGE ransomware, attributed to JADEPUFFER, leverages a Langflow RCE vulnerability to encrypt AI model files, weights, and training data.
JadePuffer Ransomware Targets AI Model Data with EncForge
JadePuffer, an autonomous AI agent, now employs EncForge ransomware to encrypt AI training datasets, vector databases, and model checkpoints, posing a significant threat…
Inc Ransomware Exploits SonicWall SMA Zero-Days for Root Access
Inc Ransomware is actively exploiting chained zero-day vulnerabilities in SonicWall SMA appliances, achieving root-level capabilities.
Diverse Threat Landscape: Military Tracking, macOS Malware, Defense Ransomware
Analysis of diverse threats including reported Iranian tracking of US military phones, CrashStealer macOS malware, ransomware on a naval firm, and a Lidl data breach.
Fairlife Ransomware Attack Halts US Dairy Production
Coca-Cola's Fairlife dairy subsidiary suffered a ransomware attack, halting US production. Understand the operational impact and defense strategies.

ThreatsDay Report: Emerging Deception & Rapid Ransomware Threats
Analysis of recent threats, including deceptive game cheat spyware, rapid ransomware deployments, and Chrome sync abuse.
Identity Attacks & MFA Bypass: The New Ransomware Entry Point
Identity-based attacks, particularly email phishing, are now the leading cause of ransomware infections.
OFAC Sanctions VPN and Crypto Services Linked to Ransomware
US Treasury sanctions Cryptex and PM2VPN for facilitating money laundering and infrastructure for ransomware gangs like LockBit and Hive.

US Sanctions 1VPNS and Cryptor Seller for Ransomware Support
US OFAC sanctions First VPN Service (1VPNS) and a malware cryptor operator for providing critical infrastructure to ransomware groups and cybercriminals.

Threat Recap: Unpatched Exploits, Citrix Bleed 2, AI Attacks
Analysis of current cyber threats including persistent unpatched vulnerabilities, the emergence of Citrix Bleed 2 ransomware, and AI's role in attacker toolchains.
Ryuk Ransomware Affiliate Pleads Guilty to US Hacking Charges
A 34-year-old Armenian national faces 15 years in prison for his role in the Ryuk ransomware operation, which targeted U.S. hospitals and businesses.
Insider Threat: Security Expert Sentenced for BlackCat/ALPHV Aid
Former ransomware negotiator Angelo Martino received a 70-month prison sentence for aiding the BlackCat/Alphv ransomware group, highlighting insider threat risks.
GodDamn Ransomware Leverages Signed Driver to Disable EDR
Analysis of GodDamn ransomware's BYOVD technique, utilizing a Microsoft co-signed driver to disable security software, impacting US companies.
Mount Royal University Data Breach: Ransomware Impact & Mitigation
Mount Royal University confirms a ransomware attack led to data theft and deletion, impacting student, employee, and university data. Review critical mitigation steps.
Accenture Confirms Breach: LockBit 2.0 Ransomware and Stolen Data
Accenture confirmed a security breach involving LockBit 2.0 ransomware, leading to 35 GB of stolen source code and proprietary data. Runtime Rebel analyzes the impact.
JadePuffer: First LLM-Driven Ransomware Leverages Langflow Flaw
Analysis of JadePuffer, the first reported LLM-driven ransomware, which exploited a Langflow vulnerability to exfiltrate database data and encrypt systems.