Advertisement
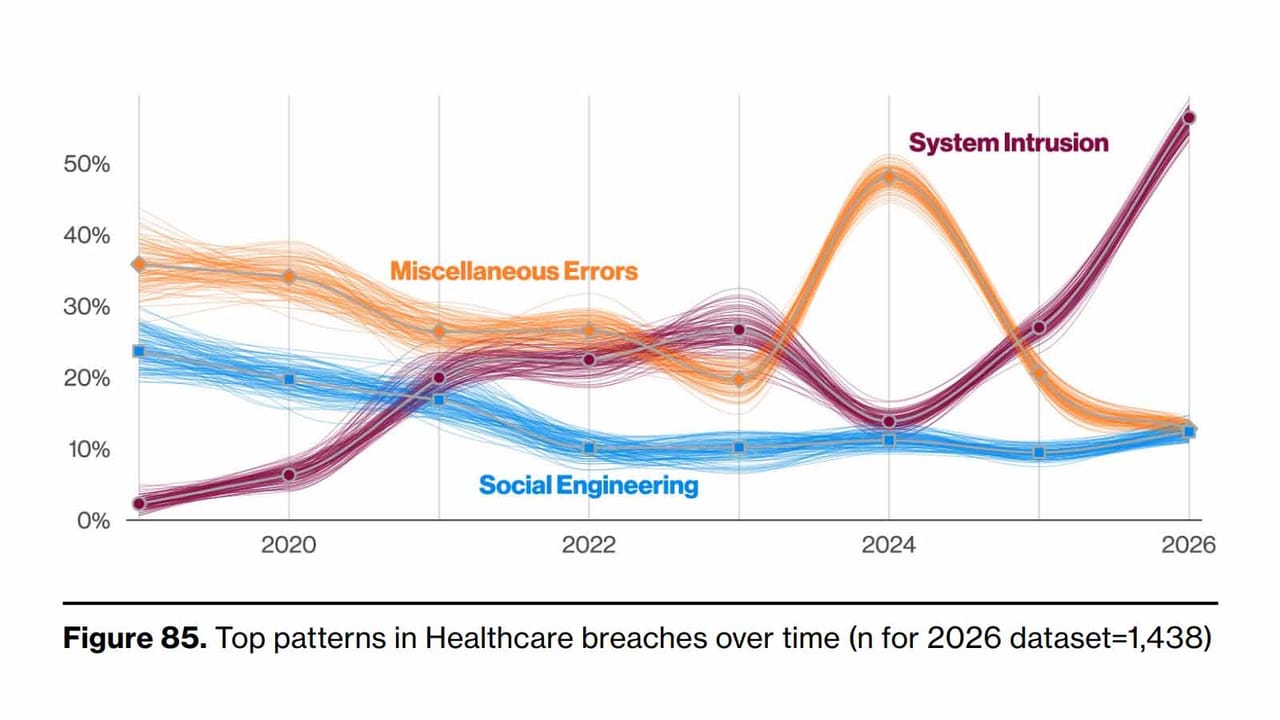
Verizon DBIR 2024: Healthcare Targeted by Social Engineering
An analysis of the 2024 Verizon DBIR healthcare findings, highlighting the surge in social engineering, ransomware, and supply chain vulnerabilities.
FBI Disrupts First VPN Service Used by Ransomware Groups
The FBI and international partners dismantled First VPN, a specialized service used by dozens of ransomware groups for reconnaissance and intrusions.
Police Seize First VPN Service Linked to Global Ransomware Attacks
International law enforcement dismantles First VPN, a bulletproof service used by threat actors for ransomware deployment and anonymous data exfiltration.
SonicWall Gen6 SSL-VPN MFA Bypass: Incomplete Patching Leads to Compromise
Hackers are bypassing MFA on SonicWall Gen6 SSL-VPN appliances via brute-force due to incomplete patching, enabling ransomware tool deployment.
DBIR 2026: Vulnerability Exploitation Now Top Breach Vector
Verizon's 2026 DBIR reveals vulnerability exploitation as the leading breach vector, surpassing credential theft.
Microsoft Disrupts MSaaS Operation Abusing Artifact Signing Service
Microsoft shuts down a malware-signing-as-a-service provider that leveraged fraudulent certificates to bypass security controls for ransomware groups.
Advertisement
Microsoft Disrupts Fox Tempest Malware Signing Service
Microsoft dismantled the Fox Tempest (Storm-1152) malware signing service, which issued over 10,000 fraudulent certificates to mask ransomware and other malware.
American Lending Center Data Breach: 123,000 Impacted by Ransomware
American Lending Center confirms a June 2023 ransomware attack compromised sensitive data of 123,000 individuals, highlighting long-term forensic challenges.

Nitrogen Ransomware Hits Foxconn: Manufacturing Cyber Crisis
Nitrogen ransomware targets Foxconn's North American plants, highlighting a critical trend of cyberattacks against the manufacturing sector's low downtime tolerance.
West Pharmaceutical Breach: Analysis of System Encryption
West Pharmaceutical Services confirms data exfiltration and system encryption in a major cyberattack. Learn about the impact and defense strategies.
Foxconn North America Ransomware Attack: Nitrogen Group Data Theft
Foxconn's North American operations confirm a ransomware attack by Nitrogen group, resulting in 8TB of data theft, including confidential documents.
Ransomware Attackers Target Backup Infrastructure to Block Recovery
Explore how ransomware operators neutralize backup systems to prevent recovery. This analysis covers attacker TTPs and mitigation steps for backups.

MuddyWater Exploits Microsoft Teams for False Flag Ransomware
Iranian APT MuddyWater is leveraging Microsoft Teams social engineering to deploy false flag ransomware, obscuring state-sponsored espionage activities.
Karakurt Extortion Gang Negotiator Sentenced to 8.5 Years in Prison
A Latvian national and key negotiator for the Karakurt extortion gang has been sentenced to 102 months for his role in U.S.-based data theft operations.

BlackCat Ransomware: Cybersecurity Pros Sentenced for 2023 Attacks
Two cybersecurity professionals receive four-year prison sentences for their roles in facilitating BlackCat (ALPHV) ransomware attacks against U.S. victims.
Quantifying Cyber Risk: CISO Budgeting with Insurance Data
CISOs now have powerful data from cyber insurance policies to quantify cyber risk, demonstrate ROI, and justify critical security investments to boards.
VECT 2.0 Ransomware Analysis: Encryption Flaws Act as Data Wiper
VECT 2.0 ransomware features a critical flaw in its encryption logic that permanently wipes large files, making data recovery impossible even with a key.

VECT 2.0 Ransomware Acts as Wiper on Windows, Linux, and ESXi
VECT 2.0 ransomware permanently destroys files over 131KB on Windows, Linux, and ESXi systems due to flawed encryption, making data recovery impossible.
Trigona Ransomware: Custom Tool for Faster Data Exfiltration
Trigona ransomware operators are employing a new custom command-line tool to accelerate data exfiltration, posing a significant threat to compromised networks.
The Gentlemen Ransomware Group: Rapid Escalation and Sophistication
An analysis of 'The Gentlemen' ransomware group, highlighting their rapid operational scaling and sophisticated attack methods impacting organizations globally.
Kyber Ransomware Targets Windows, ESXi with Post-Quantum Encryption
Kyber ransomware is encrypting Windows and VMware ESXi systems, with one variant leveraging Kyber1024 post-quantum encryption, posing new decryption challenges.
BlackCat Ransomware Negotiator Scheme: Insider Threat Implications
A ransomware negotiator's guilty plea in a BlackCat scheme highlights critical insider threat risks and the importance of stringent controls in ransom payment processes.
Security Expert Aids BlackCat Ransomware, Exposing IR Risks
A US security expert pleaded guilty to collaborating with the BlackCat ransomware group, leveraging his negotiation role.

SystemBC C2 Analysis: 1,570 Victims of The Gentlemen Ransomware
Analysis of a SystemBC C2 server linked to The Gentlemen ransomware reveals over 1,570 victims and the use of SOCKS5 tunnels for persistent access.