All Articles
Security Intelligence
3736 articles · Updated every 8 hours
Advertisement
Zyxel Fixes Critical RCE Vulnerability in UPnP Implementation
Zyxel releases patches for CVE-2024-42057, a command injection flaw in the UPnP function of several VMG and fiber router models, allowing unauthenticated RCE.
New York Sues Valve Over Alleged Illegal Gambling in Loot Boxes
The New York Attorney General sues Valve Corporation, alleging that loot boxes and skin trading ecosystems facilitate illegal gambling targeting minors.

Malicious StripeApi.Net NuGet Package Targets Financial API Tokens
Researchers identify a typosquatting NuGet package, StripeApi.Net, designed to mimic official Stripe libraries and exfiltrate sensitive financial API keys.

Microsoft Warns of Fake Next.js Repos Delivering In-Memory Malware
Microsoft warns developers of a coordinated campaign using malicious Next.js repositories disguised as job assessments to deliver in-memory malware.

Cisco SD-WAN Zero-Day CVE-2026-20127 Exploited for Admin Access
CVE-2026-20127 is a critical CVSS 10.0 flaw in Cisco SD-WAN controllers exploited since 2023, allowing unauthenticated remote administrative access.
Hypervisor-Based Persistence: Abusing Virtual Machines for Stealth
Analysis of how threat actors leverage virtualization platforms to host malicious guest OSs, bypassing host-level EDR and maintaining persistent access.
Advertisement
Optimizing Honeypot Log Analysis Using AI and LLM Orchestration
An analysis of how AI-assisted log processing reduces noise in DShield and Cowrie honeypot data, enabling analysts to identify sophisticated threat patterns.
CLAIR Model: Mapping Critical Infrastructure Interdependencies
The CLAIR Model is a conceptual framework designed to map complex interdependencies within critical infrastructure, enhancing resilience and risk assessment.
AI Code Generation Poses Supply Chain Risk to Developer Machines
Learn how AI-generated code, like from Anthropic's Claude, can introduce vulnerabilities and malicious payloads, compromising developer machines and software supply…
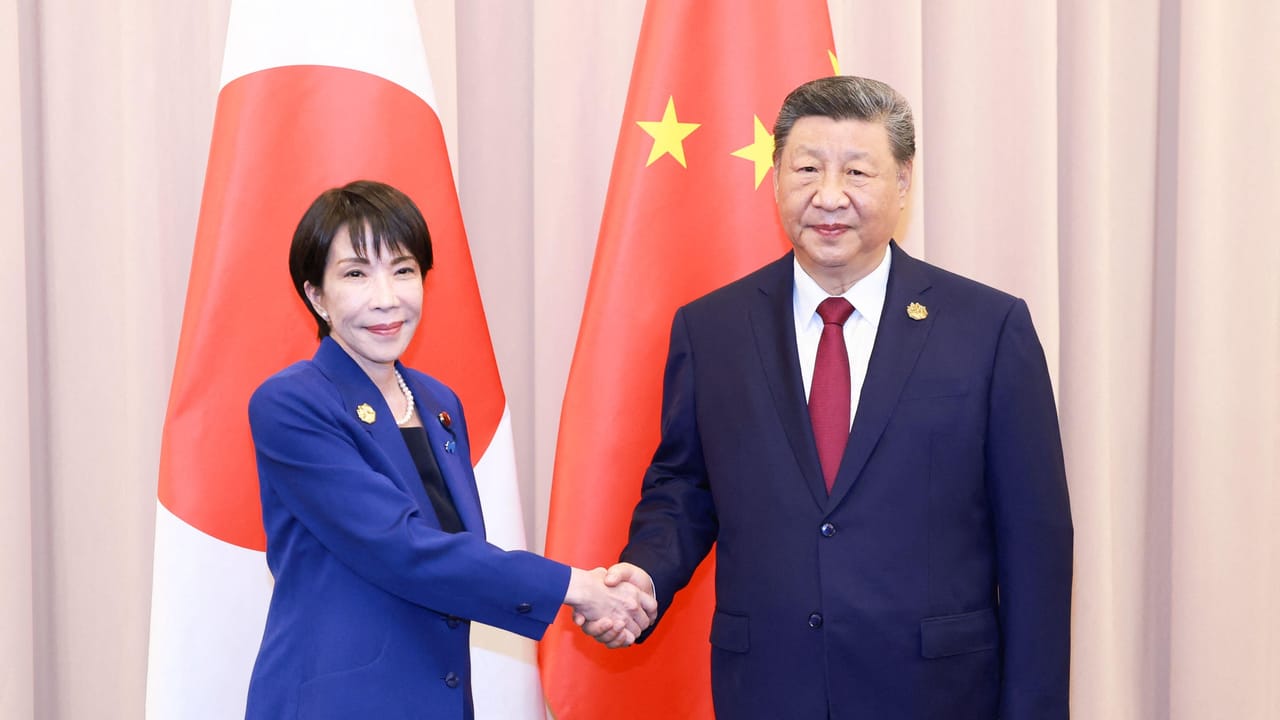
Chinese Police Use ChatGPT in Influence Operations Against Japan
Chinese police reportedly used ChatGPT for politically motivated influence operations to smear Japan's PM Takaichi, highlighting AI's role in disinformation campaigns.
Fake Next.js Job Interview Tests Backdoor Developers
Microsoft Defender discovered a campaign where malicious Next.js job interview tests backdoor developers' devices, posing a supply chain risk.
UFP Technologies Data Breach Exposes Sensitive Personal Information
Medical device manufacturer UFP Technologies confirms a February 2024 cyberattack led to the theft of Social Security numbers and personal data.
Cisco SD-WAN Exploitation: Critical Authentication Bypass & Escalation
CISA alerts on active global exploitation of Cisco SD-WAN, leveraging CVE-2026-20127 for initial access and CVE-2022-20775 for privilege escalation.
CISA Adds Two Cisco SD-WAN Exploits to KEV Catalog
CISA adds CVE-2022-20775 (Path Traversal) and CVE-2026-20127 (Auth Bypass) affecting Cisco SD-WAN to its Known Exploited Vulnerabilities Catalog.
Next.js Supply Chain Attacks: North Korean Actors Target Developers
North Korean state-sponsored actors leverage malicious Next.js repositories and fake job interviews to compromise developers' systems for persistent access and espionage.
Chinese Cyberspies Exploit SaaS APIs in Global Espionage Campaign
A suspected Chinese threat actor breached dozens of telecom firms and government agencies, using SaaS API calls to evade detection in a global espionage campaign.
Critical Cisco SD-WAN Zero-Day Exploited Since 2023
Cisco Catalyst SD-WAN critical authentication bypass (CVE-2026-20127) actively exploited since 2023, enabling remote compromise and rogue peer addition.

Claude Code Flaws Enable RCE & API Key Exfiltration
Multiple security flaws in Anthropic's Claude Code AI coding assistant allow remote code execution and API credential theft via configuration mechanisms.

Google Disrupts UNC2814 GRIDTIDE Infrastructure After 53 Breaches
Google disrupts infrastructure of China-nexus threat actor UNC2814 (GRIDTIDE) after 53 breaches across 42 countries targeting government and telecom sectors.
GRIDTIDE Espionage: PRC-Nexus UNC2814 Targets Telecoms Globally
Google disrupts GRIDTIDE, a novel backdoor used by PRC-nexus UNC2814 for global cyber espionage against telecommunications and government entities.
TOAD Emails: The 'Call This Number' Gateway Bypass Threat
Attackers use Telephone-Oriented Attack Delivery (TOAD) with 'call this number' emails to bypass gateways, relying on social engineering post-call.
Google Disrupts Chinese Espionage Actor UNC2814 Targeting Telecoms
Google and Mandiant disrupt UNC2814, a Chinese state-sponsored actor active since 2017, targeting 42 countries across telecom and government sectors.
Stolen Credentials and the Escalation of Agentic AI Attacks
IBM X-Force reports 56% of 2025 vulnerabilities require no authentication, enabling agentic AI to weaponize stolen credentials and expand attack blast radius.
OpenClaw Underground Trends: Assessing Hype vs. Operational Risk
Flare telemetry reveals a gap between high OpenClaw chatter on Telegram and actual exploitation, highlighting the need to distinguish hype from threat.