All Articles
Security Intelligence
3736 articles · Updated every 8 hours
Advertisement
Lazarus Group Shifts to Medusa Ransomware & Multi-Tool Attacks
North Korea's Lazarus Group now employs Medusa ransomware, Comebacker backdoor, Blindingcan RAT, and Infohook info stealer in recent attacks, signaling an evolving…
Attackers Halve Breakout Time to 29 Minutes, CrowdStrike Reports
CrowdStrike research indicates attackers now achieve lateral movement in just 29 minutes, driven by credential misuse, AI, and blind spots.
VMware Aria Operations RCE Vulnerability Patched
Broadcom patched high-severity vulnerabilities in VMware Aria Operations, including an RCE flaw. Organizations must update immediately to mitigate risk.
Arkanix Stealer: Rapid Disappearance of C++ & Python Malware
Arkanix Stealer, a C++ and Python-based info-stealer, emerged briefly, exfiltrating system data, browser credentials, and files before vanishing. Analysis of its TTPs.
Wynn Resorts Data Breach: ShinyHunters Exfiltrates Employee PII
Wynn Resorts confirms a data breach impacting employee PII, attributed to the ShinyHunters extortion gang. Analysis covers TTPs and mitigation strategies.
Diesel Vortex Phishing Campaign Targets Logistics Sector
Financially motivated Diesel Vortex group targets US & European freight and logistics with extensive phishing campaign, using 52 domains to steal credentials.
Advertisement

UAC-0050 Targets European Financial Institutions with RMS Malware
Russia-aligned actor UAC-0050 expands operations beyond Ukraine, targeting European financial entities with spoofed domains and RMS malware for espionage.

RoguePilot Vulnerability: GitHub Codespaces GITHUB_TOKEN Leak
Orca Security researchers discovered RoguePilot, a flaw in GitHub Codespaces allowing attackers to steal GITHUB_TOKENs through indirect prompt injection.
UK ICO Fines Reddit £14.47M Over Children's Data Privacy Failures
The UK ICO fined Reddit $19.5 million for processing data of 1.5 million children without parental consent, citing systemic age verification failures.
Mitigating Identity Risks in Autonomous AI Agent Workflows
Enterprise security must evolve to manage AI agents as non-human identities (NHIs) by implementing intent-based controls and solving over-scoped privilege risks.
Critical Flaws in PUSR USR-W610 Impact Critical Manufacturing
CISA identifies critical vulnerabilities in PUSR USR-W610 gateways, including authentication bypass and credential theft. No patches available for EOL hardware.
Valmet DNA Engineering Web Tools Vulnerable to Path Traversal
Unauthenticated attackers can exploit CVE-2025-15577 in Valmet DNA Engineering Web Tools to gain arbitrary file read access across critical infrastructure.
CISA Adds Roundcube Webmail Vulnerabilities to KEV Catalog
CISA adds CVE-2025-49113 and CVE-2025-68461 to its Known Exploited Vulnerabilities catalog, signaling active exploitation of Roundcube Webmail systems.
AI Influence Operations and the Erosion of Democratic Feedback
Bruce Schneier analyzes how AI-generated content overwhelms democratic institutions and creates an influence arms race, threatening institutional integrity.
Spanish Authorities Dismantle Anonymous Fénix Hacktivist Node
Spain's National Police arrested four members of Anonymous Fénix, a hacktivist group targeting government infrastructure with DDoS and data exfiltration.
Chinese APTs Exploit CVE-2024-34351 in TeamT5 ThreatSonar
Taiwanese security firm TeamT5 confirms that a critical command injection flaw in ThreatSonar Anti-Ransomware has likely been exploited by Chinese APT groups.
Lazarus Group Targets U.S. Healthcare with Medusa Ransomware
North Korean Lazarus Group is targeting U.S. healthcare providers with Medusa ransomware, utilizing Dtrack malware for initial access and persistence.
ShinyHunters Claims Breach of Odido Telecom Affecting Millions
The ShinyHunters extortion group claims to have exfiltrated millions of customer records from Dutch telecommunications provider Odido via a third-party breach.

UnsolicitedBooker Targets Central Asian Telecoms via LuciDoor Backdoor
The UnsolicitedBooker threat actor has pivoted to targeting telecommunications providers in Kyrgyzstan and Tajikistan using LuciDoor and MarsSnake backdoors.

Lazarus Group Deploys Medusa Ransomware in Global Healthcare Attacks
Lazarus Group (Diamond Sleet) targets Middle Eastern entities and U.S. healthcare with Medusa ransomware, according to Symantec and Carbon Black reports.

Identity Prioritization: Shifting from Backlogs to Risk Math
Enterprise identity programs must evolve from ticket-based prioritization to dynamic risk math models to manage the surge of human and non-human identities.
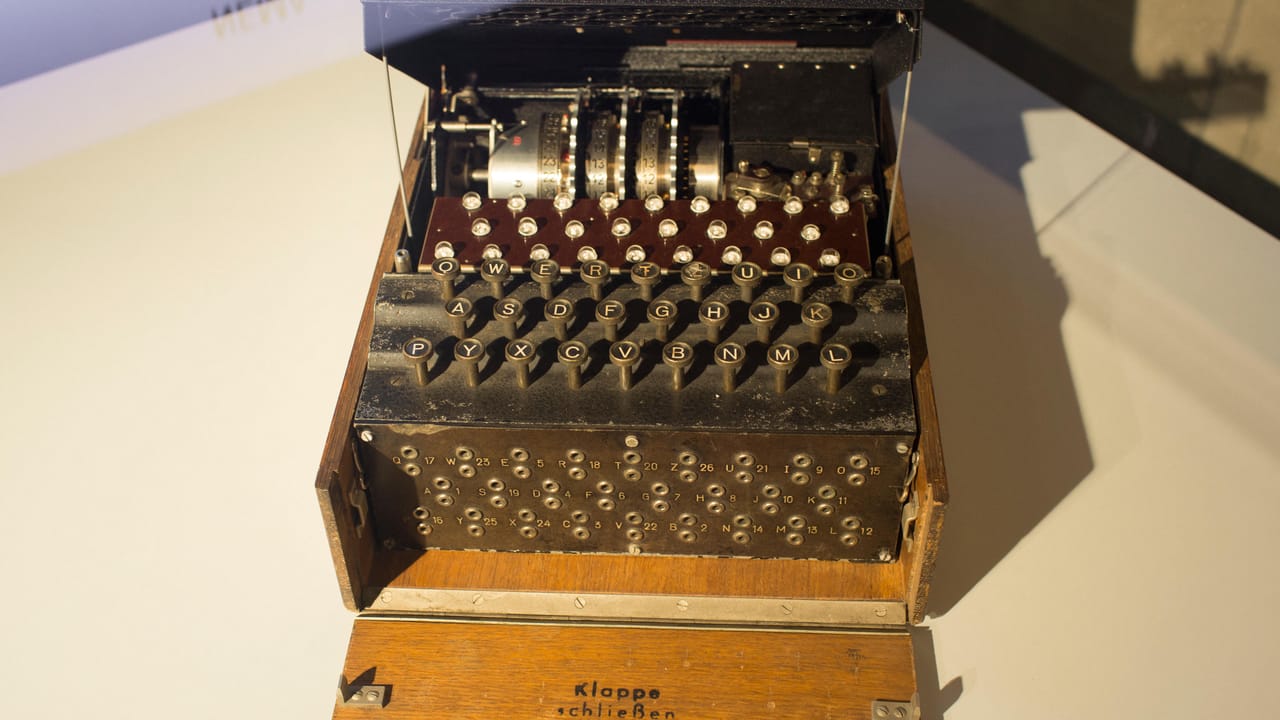
Operational Resilience: Cryptographic Lessons from the Enigma Device
An analysis of historical cryptographic failures within the Enigma machine and how these resilience errors inform modern cybersecurity defense strategies.

MuddyWater Deploys BugSleep Backdoor in Targeted Regional Campaigns
Iranian state actor MuddyWater introduces the custom BugSleep backdoor, targeting Middle Eastern and African entities using spear-phishing and RMM abuse.
ATM Jackpotting Trends: $20M Losses Driven by Legacy Exploits
ATM jackpotting surged in 2025, resulting in over $20 million in losses as threat actors leverage decade-old tools and black-box tactics against aging hardware.